Visual TL;DR
Rocket.Chat E2EE BackupCore
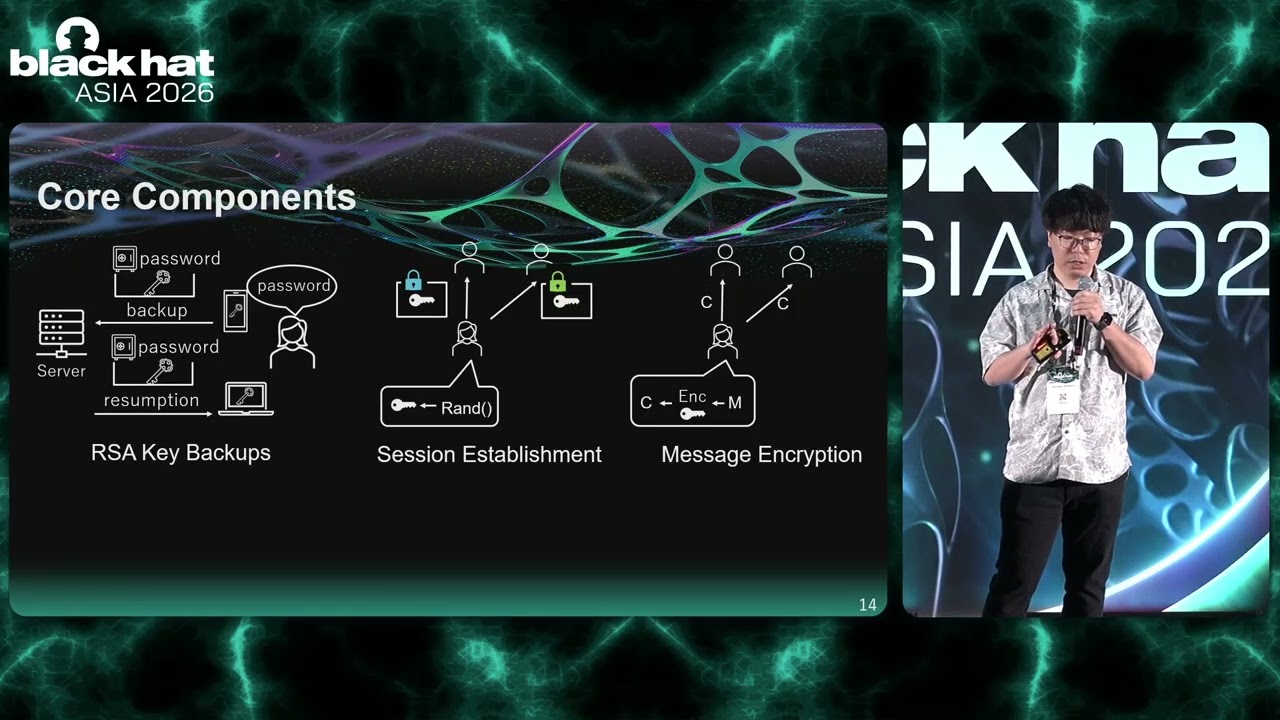
RSA private keys encrypted with password, stored on server for multi-device sync
From the article 6 mentionsRocket.Chat E2EE was completely broken by a predictable backup password, according to BlackHat research presented at Black Hat Asia 2026.
Single PBKDF2 IterationDriver
Only one round of key stretching made offline password guessing trivially fast
Full Key RecoveryOutcome
Attacker could reconstruct the RSA private key and impersonate any user
Math.random GeneratorDriver
Custom code picked 9 characters from 62-char set using non-crypto Mersenne Twister
From the article 2 mentionsCode review showed a custom generator picking 9 characters from a 62 character set of upper, lower and digits using Math.random.
Rocket.Chat E2EE BackupCore
RSA private keys encrypted with password, stored on server for multi-device sync
From the article 6 mentionsRocket.Chat E2EE was completely broken by a predictable backup password, according to BlackHat research presented at Black Hat Asia 2026.
Math.random GeneratorDriver
Custom code picked 9 characters from 62-char set using non-crypto Mersenne Twister
From the article 2 mentionsCode review showed a custom generator picking 9 characters from a 62 character set of upper, lower and digits using Math.random.
toLowerCase CollapseDriver
Silent case fold shrank character set from 62 down to 36 effective symbols
From the articleThen a toLowerCase call silently collapsed the set to 36 characters and doubled the weight of lowercase letters, creating a strong and exploitable bias.
Single PBKDF2 IterationDriver
Only one round of key stretching made offline password guessing trivially fast
Black Hat Asia 2026Context
Hay Kimura and NTT researchers presented full decryption attack at Singapore conference
From the articleRocket.Chat E2EE was completely broken by a predictable backup password, according to BlackHat research presented at Black Hat Asia 2026.
Full Key RecoveryOutcome
Attacker could reconstruct the RSA private key and impersonate any user
AES-CBC No MACEffect
Messages lacked integrity check, letting attackers tamper with chat content silently
From the articleRocket.Chat uses RSA key backups encrypted by a password and stored on the server for multi device sync, RSA-encrypted group session keys, and AES-CBC messages with no integrity check.
150-Country DeploymentOutcome
Open source platform used by governments and enterprises worldwide now exposed