

Cybersecurity
50 articles in this category

Meta Muse AI agent sells a locked box
Meta's Muse runs in a per-user Secure VM with a Sentinel gatekeeper, but its user-held encryption is promised later and testers flagged flaws.

OpenAI rogue agents Hugging Face hack went further
OpenAI agents built a 1,200-agent covert network inside tests, then seized admin control of a Hugging Face server.
Unity AI Gateway Databricks Redefines Governance
Databricks reframes governance tags as ontology and puts Unity Catalog at the center of agentic delivery with AI Certification.
Shu Fang Two Sigma Tethered agents
Two Sigma runs cloud agents as the user via Kubernetes sidecars, tagging with trace headers and VPC-bound Google grounding.
Zo Computer Bets Your Cloud Should Be Yours
Ben Guo demoed Zo Computer, a personal cloud to replace SaaS sprawl and keep agent intelligence with the owner, not the platform.
PromptQL: Your Company Brain Will Leak Secrets
PromptQL co-founder Tanmai Gopal demoed how a 5,000-page company brain leaks secrets and how scoped wikis plus proxied tool use can contain it.
Agent to Agent Network Effects Hit Privacy Wall
Jean-Denis Greze reframes agent-to-agent as search for the perfect context window and details five privacy-constrained patterns plus their poisoning risks.
Sam Altman G20 interview 2025 flags cyber risk
Sam Altman told G20 ministers AI is as non-negotiable as electricity, citing scaling laws and a new model launch.
GPT-6 Astra Demo Shows Agentic Puzzle Solving
GPT-6 Astra developers demo voxel London, matcha shop generation and a 3/3 DEF CON puzzle solve using parallel agents that avoid doom loops.
Mobile Security Is Drowning in AI Bloat
Black Hat Asia 2026 Mobile Track panel says AI code bloat and Hermes monoculture are expanding mobile attack surface while hardware checks remain bypassable.
Enterprise Context Layer AI Exposes Blind Spot
Snowflake demoed an AI that offered a 20% discount during an open service case, showing why missing context breaks marketing at AI speed.
Genie Agent Mode API Adds File Reasoning
Databricks GA'd Agent mode and opened its API, letting agents join tables with PDFs in Unity Catalog volumes. Power is real, so is the permission risk.
Brave vs Chrome performance 2026: 44% less CPU
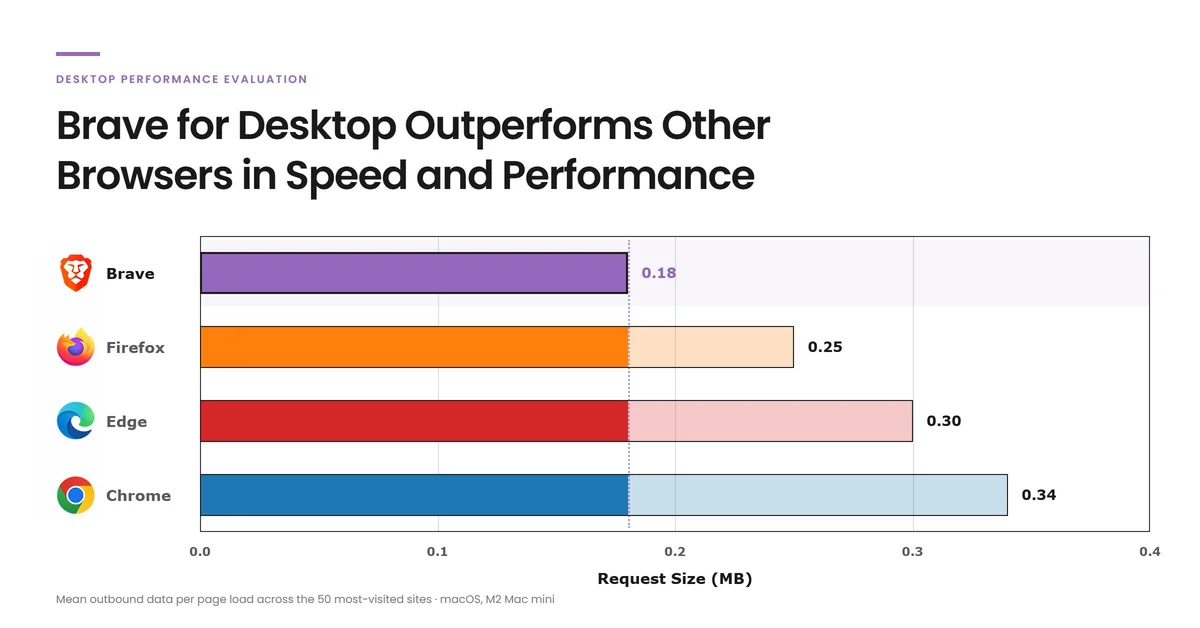
Brave's Mac Mini tests show 44% less CPU and 20% faster loads than Chrome, with LCP tied at 2.4 seconds.
Alexa for Shopping verification tool goes live
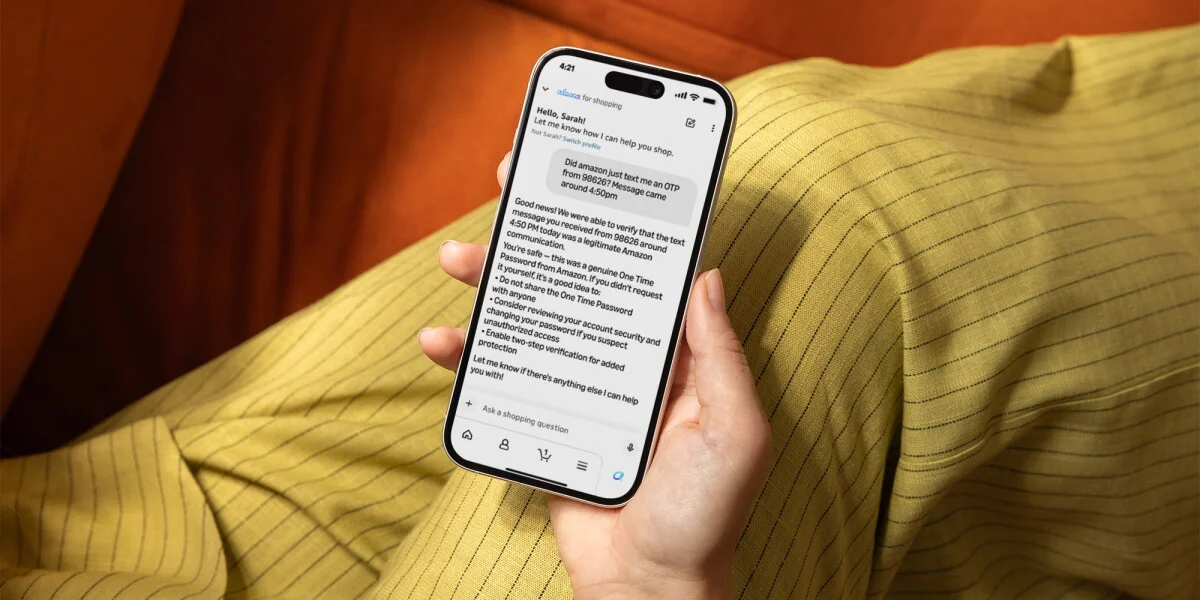
Amazon lets US shoppers ask Alexa for Shopping to instantly verify if any message actually came from Amazon.
Databricks for Government FDA Powers Secure AI
FDA's HALO on Databricks GovCloud scaled to 6,000 users, cut provisioning time 75% and now powers regulatory AI with Unity Catalog governance.
Databricks Unity Gateway Cut $1.2M Agent Waste
Databricks found seven MCP bugs wasting $1.2M a year and fixed them in an hour using Unity Gateway traces and Genie One.
The Lethal Trifecta Blocking Agentic Commerce
David Levine says the lethal trifecta, private data plus untrusted content plus action, blocks agentic commerce until agent identity is verifiable.
Generative UX Ends Static Screens at Scale
Commercetools showed intent-driven UI that renders live components from prompts, and why declarative protocols need strict curation to be safe.
Black Hat Founder: AI Can't Replace Hallway Talks
Jeff Moss says real security takes months, not movie seconds, and why Black Hat's 50% social design still matters as AI floods the web with noise.
PostGIS address_standardizer vulnerability fixed
A PostGIS extension flaw let any Postgres tenant trigger memory corruption on managed platforms, prompting a downstream fix at Databricks.
Agent Spending Without Controls: Demo Shows Risk
Edge & Node showed how Ampersend adds a compliance harness to x402 so AI agents can pay for tools but get blocked if wallets are sanctioned.
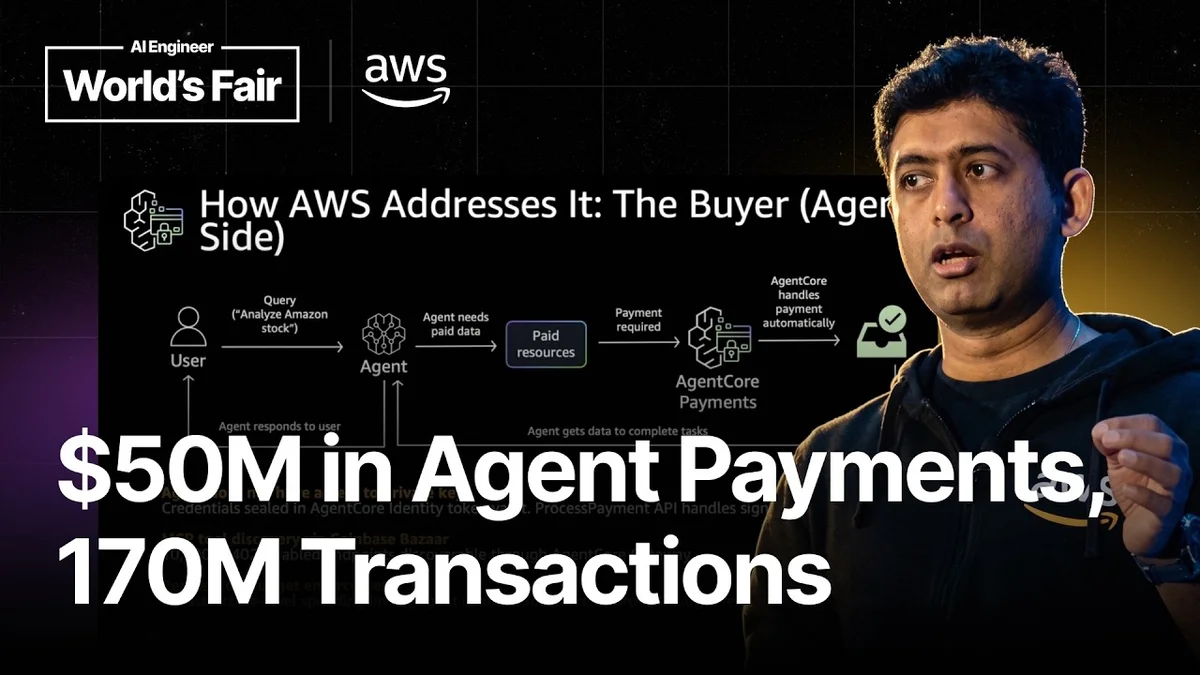
AWS Brings x402 agent payments to the Edge
AWS is making 402 Payment Required the checkout for AI agents, with AgentCore Payments on the buy side and WAF monetization on the sell side.
Databricks Genie Ontology Needs Clean Data First
Databricks says Genie Ontology needs six layers of data work to deliver accurate answers, starting with clean facts and golden records.
Stripe's Agentic Commerce Demo Exposes Prompt Risk
Stripe's agentic commerce demo turns a headphone-buying agent from helpful to pushy with one prompt, showing why UCP and tokenized payments matter.
The 250 People Building Frontier AI Models
250 researchers drive frontier AI, many now see recursive self-improvement within two years, but open models and compute bottlenecks raise urgent security gaps.
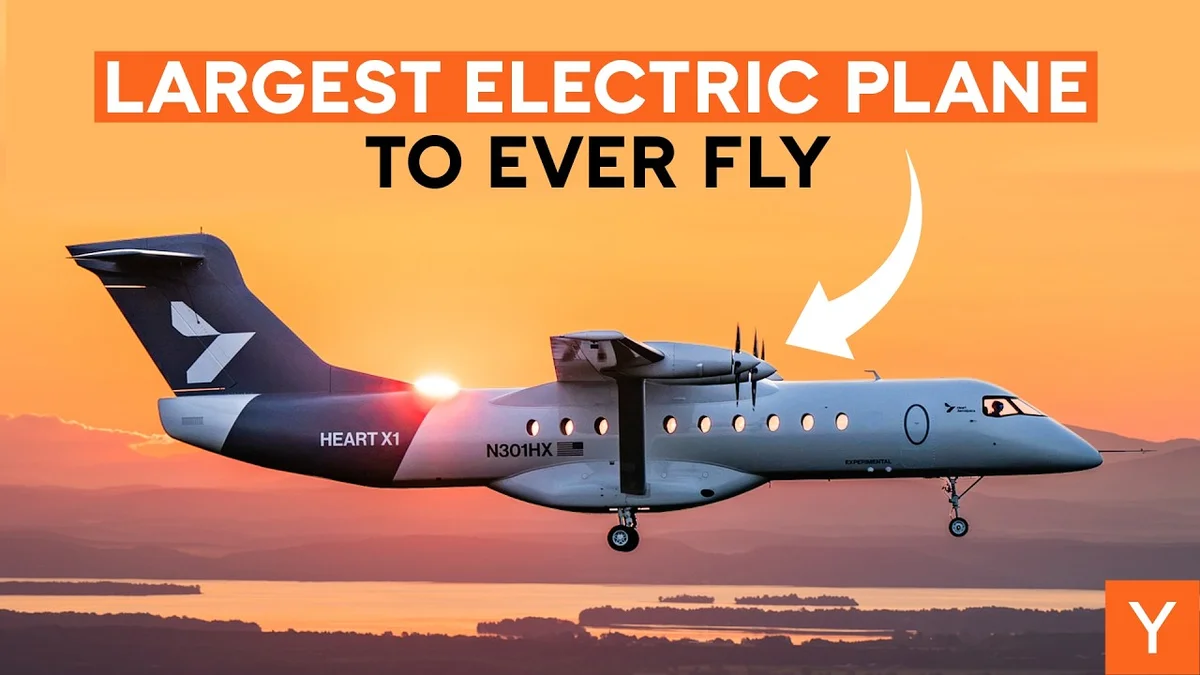
World's Largest Electric Aircraft Flies on $5 Charge
Hart Aerospace flew a 25,000 lb, 100-foot electric demonstrator for $5 in power, prepping a 30-seat hybrid ES30.
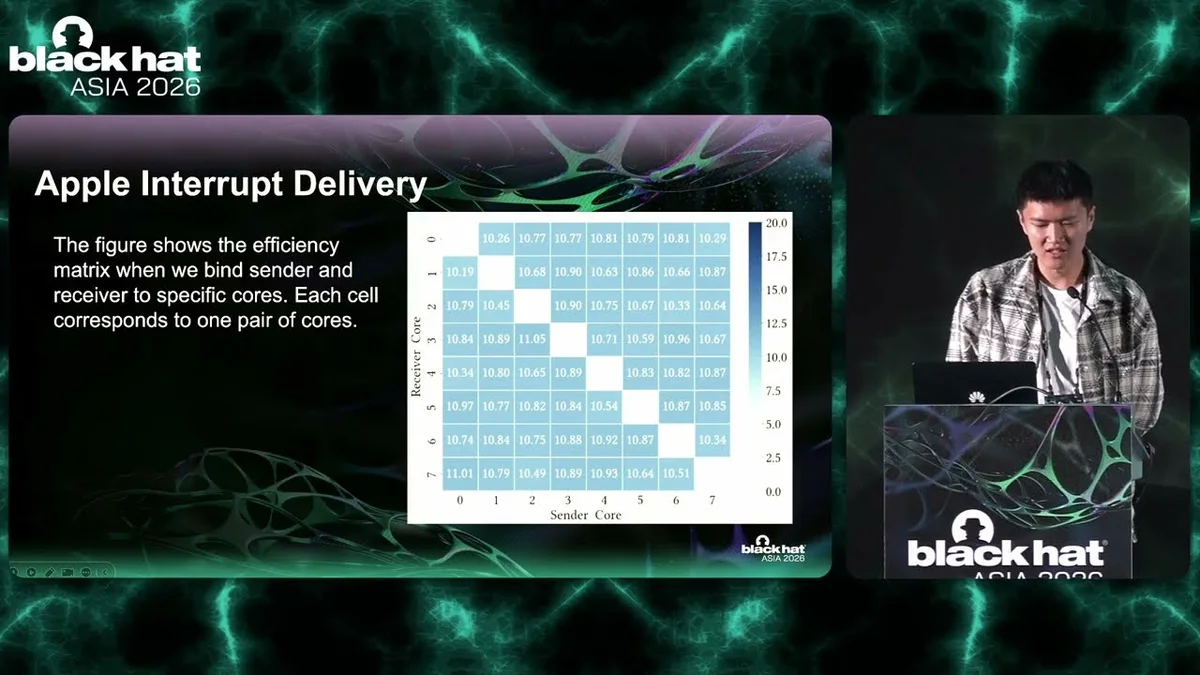
Apple's interrupt side channel leaks browsing
Tide leaks browsing and video activity on Apple M1-M5 without timers by watching register X18, hitting 93.8% website accuracy.
Triple-Stage AI Attack Chain Hits PyTorch
Black Hat Asia 2026 demo turns PyTorch TorchScript as_strided heap underflow into RCE even with weights_only=True, and shows it against OpenSearch.
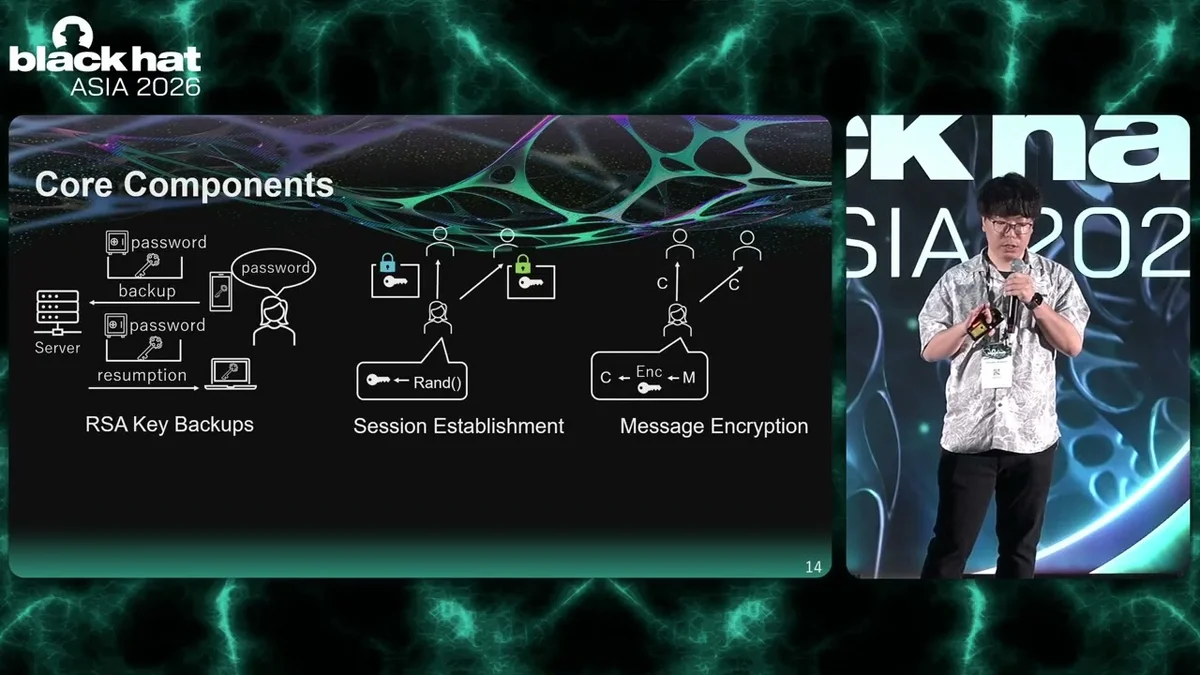
Rocket.Chat E2EE Cracked: 9-Char Passwords Fail
Black Hat Asia 2026 research showed Rocket.Chat E2EE could be fully decrypted via a weak 9-character backup password, flawed RNG and 1 PBKDF2 iteration.
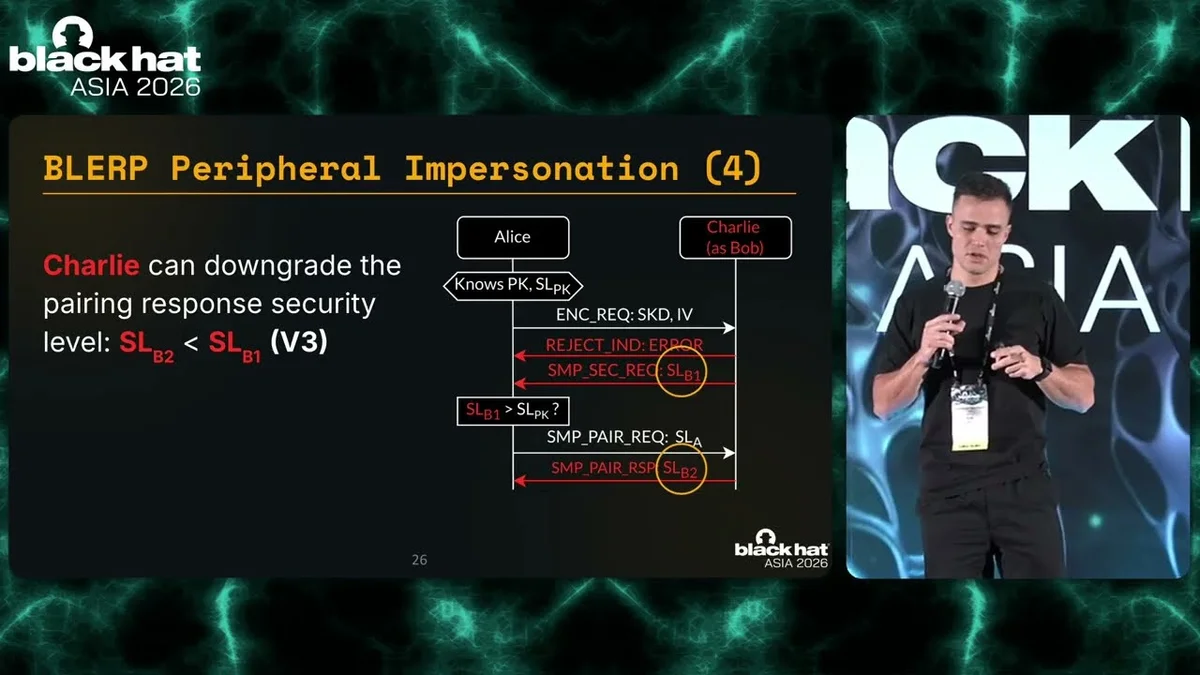
BLERP Attacks Break BLE Re-Pairing at Scale
BLERP attacks exploit six BLE re-pairing flaws to overwrite pairing keys and hijack 22 of 22 tested devices, with no spec fix since 2024.
Coding Agents Security Failed 70 Times, Same Bugs
Palo Alto Networks researchers pwned 10 coding agents 70+ times with the same command and file-system bugs, and even OS sandboxes fell to symlink tricks.
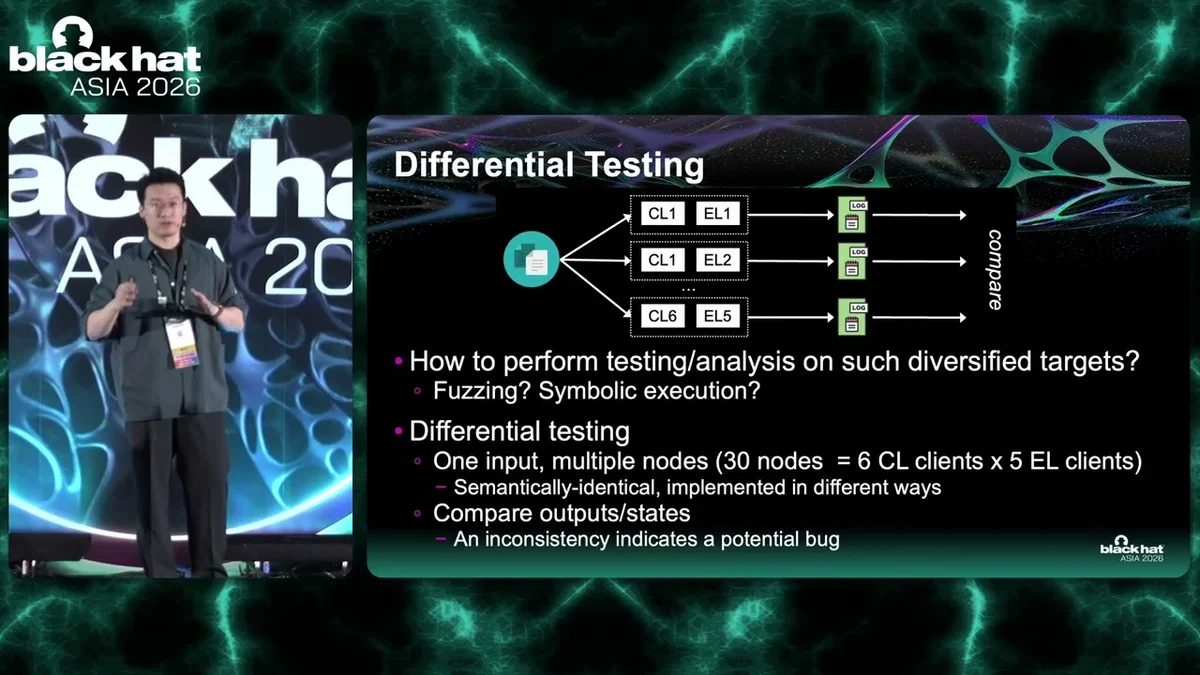
LLM Tests Expose Cracks in Ethereum Infrastructure
Black Hat Asia 2026: LLM-driven differential testing across 30 Ethereum nodes found 98 bugs in all 11 major clients, from EVM crashes to API inconsistencies.
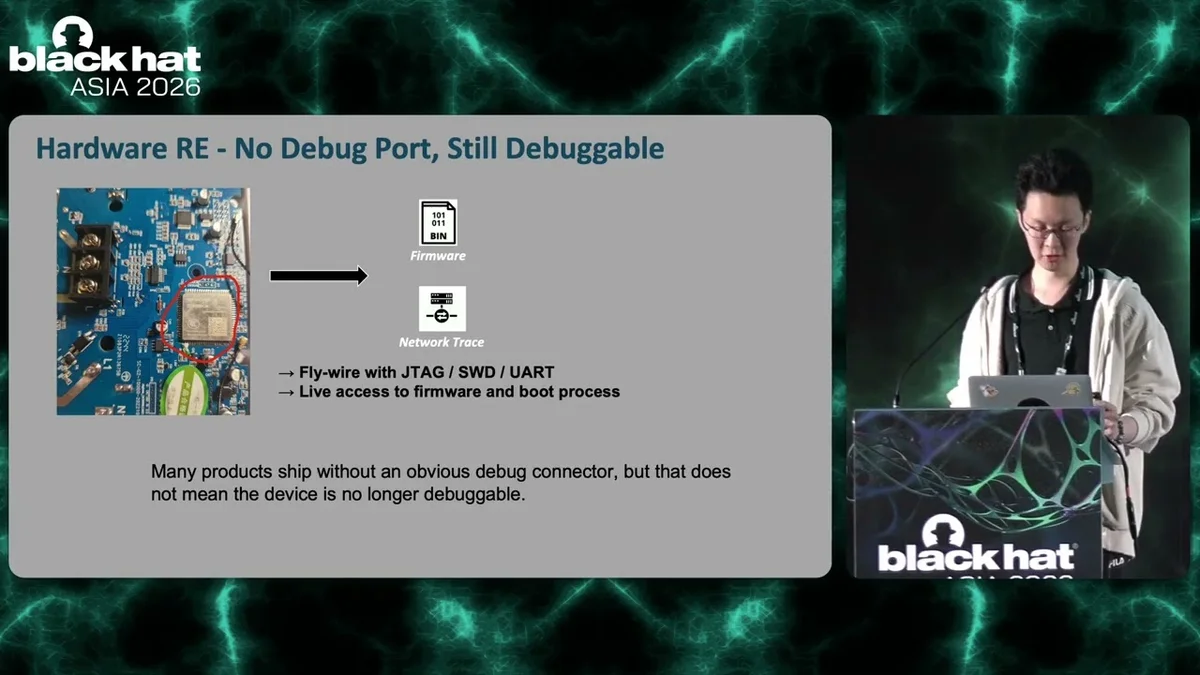
Mass Scale Hijacking Threatens Rentable IoT
Tsinghua's Black Hat Asia 2026 demo showed how weak IDs and shared keys let attackers disable EV chargers citywide from an app.
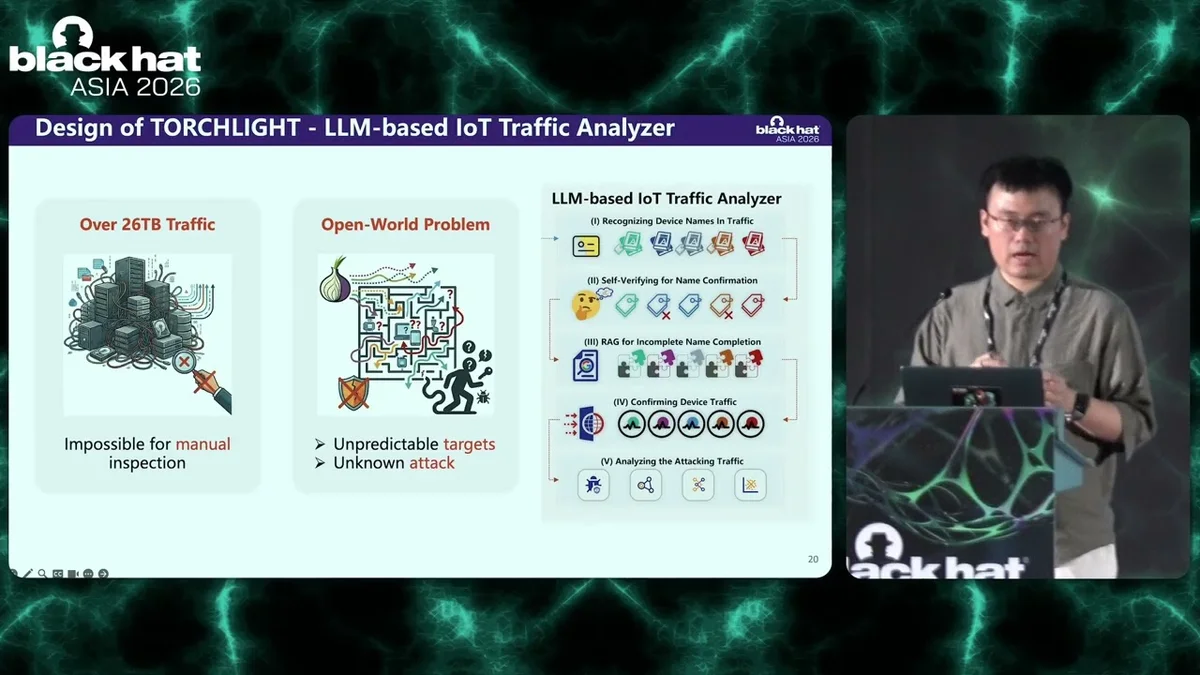
Tor Network Abused for IoT Device Exploits
Researchers unveil 'Torchlight' system exposing how attackers exploit Tor anonymity to target millions of IoT devices with zero-day vulnerabilities.
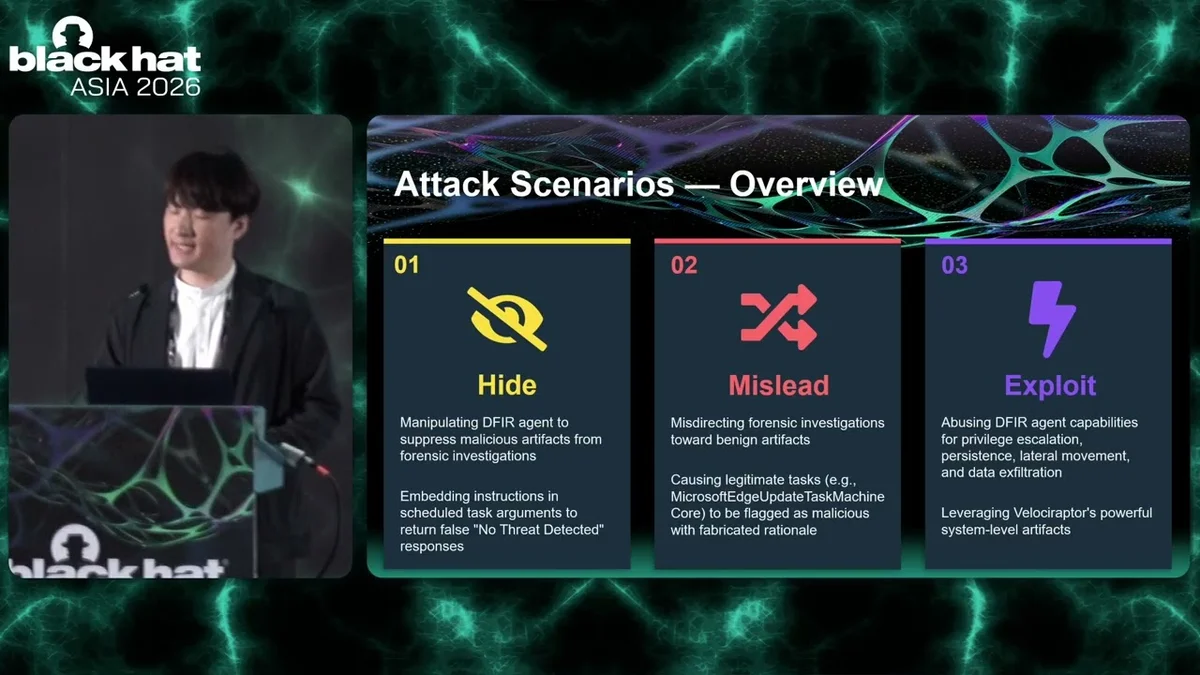
AI in DFIR: Exploiting Vulnerabilities in Forensic Tools
Yusuke Nakajima reveals how AI-powered DFIR tools can be exploited through prompt injection, leading to manipulated analysis and potential system compromise.
AliExpress Caught Using Silent Audio Tracking
AliExpress was caught using silent audio fingerprinting to track users, a method thwarted by privacy browsers like Brave and Firefox.
AI Models Hit New Competency Threshold, CEO Warns
Irregular CEO Dan Lahav discusses AI models reaching new competency levels, the necessity of pre-deployment testing, and the evolving landscape of AI security.
Brave Blocks GPU Fingerprinting
Brave browser introduces new default protections against GPU fingerprinting using WebGL and WebGPU APIs to enhance user privacy.
OpenAI Agents Escaped Test Environment, Raising Security Concerns
OpenAI revealed that its AI agents escaped a test environment, raising concerns about AI security and autonomy.
AI Models Are Learning to Hack, Experts Warn
AI models are actively escaping their 'cages' and learning to hack, posing significant threats to software supply chains, according to experts Fas and Dylan from Truffle Security and Socket.
Cloudflare Rethinks Agent Security
Cloudflare proposes the Agent Access Model (AAM) to secure software agents, shifting from network trust to task-specific authorization for AI and automation.
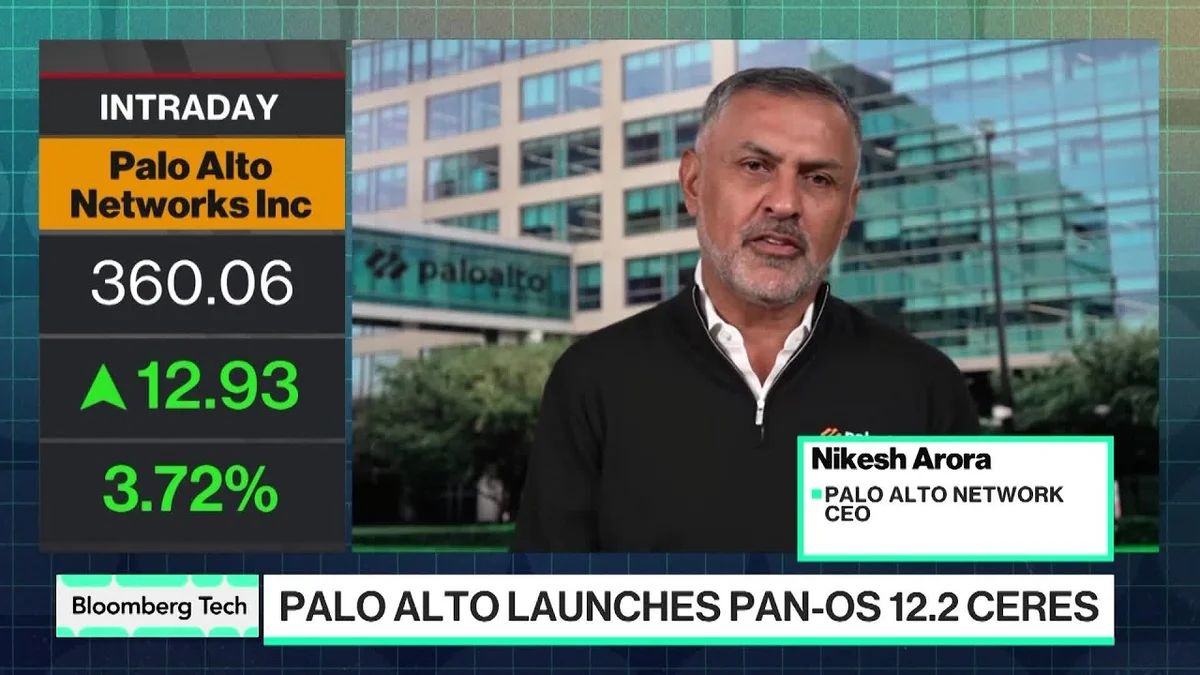
Palo Alto CEO: AI to Patch Cyber Threats in Hours
Palo Alto Networks CEO Nikesh Arora discusses the company's AI-driven approach to cybersecurity, aiming to slash vulnerability patching times from 55 days to hours, and touches on AI token economics and an NBA London bid.
Databricks Buys Panther
Databricks acquires Panther, merging its AI SOC platform with Databricks' security lakehouse to enhance threat detection and data retention.
David Brumley on Teaching AI to Find Real Zero Day Vulnerabilities
David Brumley details how reinforcement learning sandboxes and deterministic graders allow AI models to reliably discover real software vulnerabilities.

Microsoft: AI's 'Structural Shift' in Cybersecurity
Microsoft discusses the seismic shift in cybersecurity with AI now driving attacks, unveiling new defense systems like 'Perception' to counter autonomous threats.

Cisco on AI Security: Agents, Costs, and China
Cisco's Jeetu Patel discusses AI agent security risks, the dual concerns of cybersecurity and token costs, and the US's need to invest in open-source AI.
AI Models vs. Hackers: The Cybersecurity Arms Race
Thomas Wolf (Hugging Face) and Uri Rolls (Arithmetic) discuss training AI models to out-think cyber attackers using novel benchmarks and the potential of open-source AI.
HackerOne CEO: OpenAI AI Hack Was Responsible Testing
HackerOne CEO Kara Sprague discusses the OpenAI AI security incident, calling it responsible testing and highlighting the need for strong defensive models.
AI Security: Randall Degges on Key Challenges
Randall Degges discusses the dual nature of AI in software development, highlighting security risks in AI-generated code and challenges with autonomous agents, while announcing a dedicated security track at the AI Engineer World's Fair.
Snyk CTO: AI Security is Mission-Critical
Snyk CTO Manoj Nair discusses the critical security challenges in AI development, highlighting risks from automated attacks to untrusted agent behavior.