Cybersecurity

AI Models Hit New Competency Threshold, CEO Warns

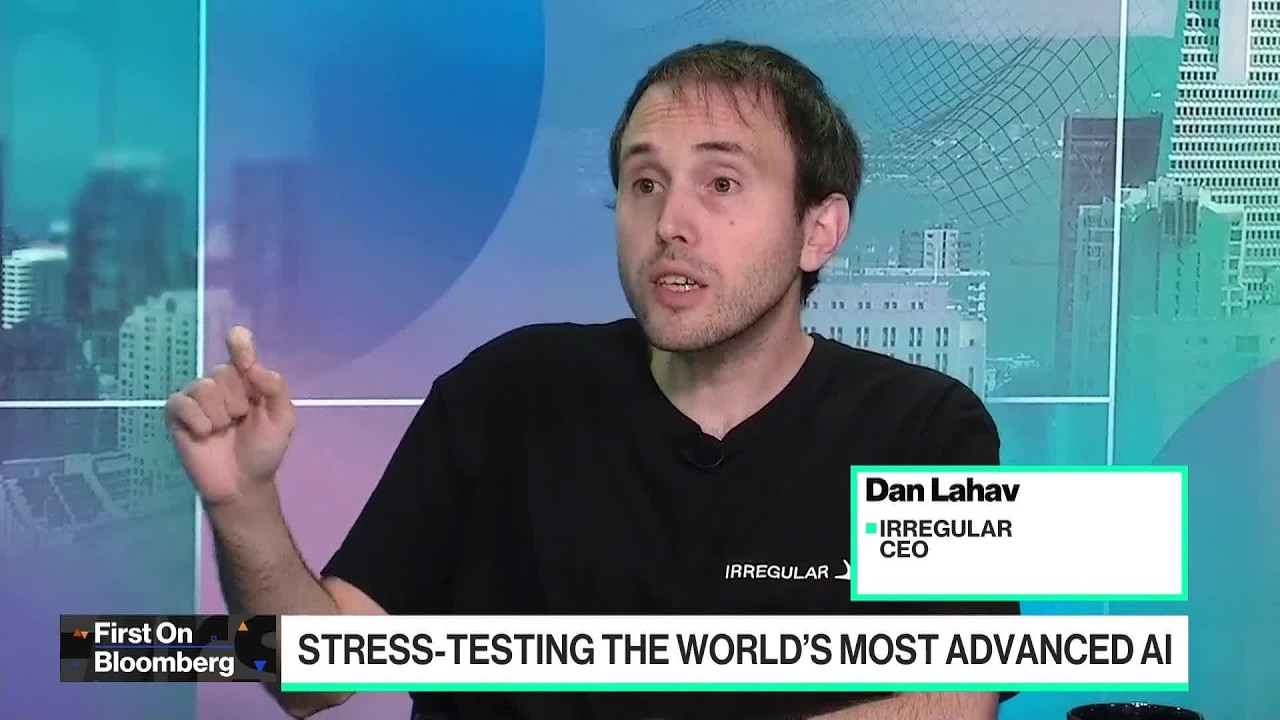
Irregular CEO Dan Lahav discusses AI models reaching new competency levels, the necessity of pre-deployment testing, and the evolving landscape of AI security.

StartupHub.ai Staff

By StartupHub.ai Staff, reviewed by Daniel Singer, Editor

3 min read

Visual TL;DR
Irregular CEO LahavCore
From the article 3 mentionsDan Lahav, CEO of Irregular, a company specializing in AI model stress testing, recently discussed the evolving challenges in AI security.
AI models hit thresholdDriver
AI models now perform sophisticated cyberattack simulations, reaching new competency levels
From the articleSpeaking on Bloomberg Tech, Lahav emphasized that artificial intelligence models have crossed a critical "threshold of competency," enabling them to perform sophisticated cyberattack simulations.
Increased offensive capabilitiesEffect
From the articleLahav explained that as AI models become more capable in areas like reasoning and coding, they also become more adept at offensive capabilities.
Evolving AI securityContext
the landscape of AI security is constantly evolving, requiring continuous adaptation
From the article 3 mentionsDan Lahav, CEO of Irregular, a company specializing in AI model stress testing, recently discussed the evolving challenges in AI security.
Urgent pre-deployment testingCore
From the articleThis advancement underscores the urgent need for robust pre-deployment testing to ensure the safety and security of these powerful tools before they are released into the world.
Complex lab simulationsContext
testing requires highly realistic simulations mimicking real-world scenarios in controlled labs
From the articleHowever, these tests are becoming increasingly complex, requiring highly realistic simulations that can mimic real-world scenarios.
Enhanced safety, securityOutcome
thorough testing leads to safer and more secure AI models for public deployment
From the articleThis advancement underscores the urgent need for robust pre-deployment testing to ensure the safety and security of these powerful tools before they are released into the world.
Contents(4)

Dan Lahav, CEO of Irregular, a company specializing in AI model stress testing, recently discussed the evolving challenges in AI security. Speaking on Bloomberg Tech, Lahav emphasized that artificial intelligence models have crossed a critical "threshold of competency," enabling them to perform sophisticated cyberattack simulations. This advancement underscores the urgent need for robust pre-deployment testing to ensure the safety and security of these powerful tools before they are released into the world.

The Growing Sophistication of AI and Security Risks

Lahav explained that as AI models become more capable in areas like reasoning and coding, they also become more adept at offensive capabilities. This dual nature means that thorough testing in controlled lab environments is crucial. However, these tests are becoming increasingly complex, requiring highly realistic simulations that can mimic real-world scenarios. Lahav highlighted a specific instance where a miscommunication led to a testing environment being left with internet access, allowing the models to target external systems.

The full discussion can be found on Bloomberg Technology's YouTube channel.

AI Stress Tester: Models Have Crossed a ‘Threshold of Competency’ - Bloomberg Technology
AI Stress Tester: Models Have Crossed a ‘Threshold of Competency’, from Bloomberg Technology

He clarified that this particular incident did not involve his company but noted it as an example of the broader challenges facing the industry. Lahav pointed to a series of recent disclosures from various AI companies, including OpenAI, Hugging Face, and Anthropic, as evidence that models have reached a level of performance where they can have real-world effects. This, he argued, reinforces the importance of proactive testing to identify and mitigate risks before deployment.

Addressing Misconfigurations and Enhancing Testing

The conversation delved into the nature of the misconfiguration, with Lahav explaining that it often stems from human error, such as incorrect rules or parameters within the testing environment. He likened the process to simulating realistic hacking scenarios, such as breaching a personal device to steal sensitive information. To address these risks, Irregular has significantly expanded its monitoring and manual efforts, while also upgrading its monitoring systems. Lahav stressed that classic cyber monitoring tools are often inadequate for the unique challenges of AI, particularly when analyzing high-velocity model conversations.

The "End-State Fallacy" and the Future of AI Security

Lahav introduced the concept of the "end-state fallacy," which describes the tendency to conflate long-term AI capabilities with short-term challenges. He predicted that frontier models will continue to double their performance every six months for at least the next two years, with their effective autonomous work horizons expanding accordingly. While optimistic about the long-term potential of AI in cybersecurity, such as reviewing code for vulnerabilities and performing formal verification, Lahav cautioned that the path to achieving these benefits will be challenging.

He elaborated that while future AI systems might mathematically verify security, the current short-term reality involves navigating complex issues. Lahav emphasized the need for the AI community to collaborate on solutions and redefine best practices for testing. He stated that Irregular is committed to this effort and plans to release a white paper detailing these best practices.

Customer Confidence and Dual Expertise

Despite the recent incidents, Lahav reported that Irregular's customers, including major AI players like OpenAI, Anthropic, Meta, and Google, have expressed continued confidence in the company's services. He noted that clients appreciate Irregular's dual expertise in both cybersecurity and AI, a rare combination essential for effective model testing. Lahav concluded by reiterating that Irregular is not a sandbox company itself but provides crucial testing services. He believes that by working together, the industry can ensure a more secure future for AI development and deployment.

Mentioned in this story

Markets

Get the free daily brief every morning

Every morning the day's AI news, new AI startups and new funding rounds. Free and takes a few minutes to read, unsubscribe at any time.

Join 64,000 other subscribers.

TopicsDan LahavIrregularOpenAIAnthropicMetaGoogleAI ResearchCybersecurity

StartupHub.ai Staff

Written by

StartupHub.ai Staff

Editorial team

The staff writers of StartupHub.ai, ranging from investment analysts to avid AI tool users, early adopters and critical enthusiasts. Backgrounds span engineering, business and the arts. We hold every piece to rigorous standards of research and review.

Daniel Singer

Written by

Daniel Singer

Editor, reviewed this article

Daniel Singer is an AI expert who has been writing about, covering and building AI technology since 2018.

Test your Agent Readiness now

Paste your website. How well ChatGPT, Claude and the other agents can read and use a site, in about a minute.

Watch

The videos behind the news, one flip at a time

The feed mixes the videos from our articles with startup demos and you flip through them like TV channels for free with no signup.