Apple's interrupt side channel leaks browsing

Tide leaks browsing and video activity on Apple M1-M5 without timers by watching register X18, hitting 93.8% website accuracy.

Close-up of Apple Silicon die and MacBook running side channel trace visualization
Tide detects interrupts via X18 heartbeat on M1-M5 to fingerprint browsing activity.· BlackHat
Visual TL;DR
Interrupt side channelDriver
leaks keystrokes, packets, and video chunks without timers or clocks on Apple Silicon
From the article 2 mentionsApple Silicon's interrupt side channel leaks what you type and browse without timers, clocks or privileges, according to BlackHat Asia 2026 research.
Tide attackCore
BlackHat Asia 2026 research watches a single register across M1 to M5 Macs
From the article 4 mentionsThe attack, called Tide, hit Apple (NASDAQ:AAPL) M1 through M5 Macs and iPhone 16 Pro by watching a single register.
Browsing activity leakedEffect
reaches 93.8% accuracy on website fingerprinting and identifies video playback patterns
X18 heartbeatContext
register X18 changes value on each interrupt, acting as a timer-free signal
From the article 7 mentionsARM's AAPCS64 defines X18 as the platform register reserved for OS use, and Apple documents it as off-limits to apps.
Mitigation gapOutcome
Apple disclosed the issue but no fix shipped yet for affected Macs and iPhones
From the article 4 mentionsThe tested user-space mitigation injected thousands of fake network interrupts per second at random intervals, cutting website fingerprinting to about 60% accuracy at roughly 10% overhead.
Interrupt side channelDriver
leaks keystrokes, packets, and video chunks without timers or clocks on Apple Silicon
From the article 2 mentionsApple Silicon's interrupt side channel leaks what you type and browse without timers, clocks or privileges, according to BlackHat Asia 2026 research.
Timers no longer workContext
macOS hides /proc/interrupts and Apple Silicon lacks UMWAIT and segment registers
Tide attackCore
BlackHat Asia 2026 research watches a single register across M1 to M5 Macs
From the article 4 mentionsThe attack, called Tide, hit Apple (NASDAQ:AAPL) M1 through M5 Macs and iPhone 16 Pro by watching a single register.
X18 heartbeatContext
register X18 changes value on each interrupt, acting as a timer-free signal
From the article 7 mentionsARM's AAPCS64 defines X18 as the platform register reserved for OS use, and Apple documents it as off-limits to apps.
Unprivileged attackerOutcome
any local user process without root or special permissions can run the attack
From the articleOn Linux an unprivileged attacker could read /proc/interrupts, and on x86 UMWAIT or segment-limit tricks could expose the gap when EL0 is preempted to EL1.
Cross-core interrupt spreadDriver
interrupts propagate from performance cores to efficiency cores on Apple silicon
From the articleApple Silicon spreads shared peripheral interrupts uniformly across active cores only.
Browsing activity leakedEffect
reaches 93.8% accuracy on website fingerprinting and identifies video playback patterns
Mitigation gapOutcome
Apple disclosed the issue but no fix shipped yet for affected Macs and iPhones
From the article 4 mentionsThe tested user-space mitigation injected thousands of fake network interrupts per second at random intervals, cutting website fingerprinting to about 60% accuracy at roughly 10% overhead.
Contents(6)

Apple Silicon's interrupt side channel leaks what you type and browse without timers, clocks or privileges, according to BlackHat Asia 2026 research.

Apple's interrupt side channel leaks browsing - BlackHat
Apple's interrupt side channel leaks browsing, BlackHat

The attack, called Tide, hit Apple (NASDAQ:AAPL) M1 through M5 Macs and iPhone 16 Pro by watching a single register.

Why timers no longer stop this class of leak

Side channel research shifted from power and timing on smart cards in 1996 to Spectre and Meltdown in 2018, which proved speculation and hardware optimization could leak remotely.

Interrupt timing later joined that list, because keystrokes, packets and video chunks each create distinct interrupt patterns.

On Linux an unprivileged attacker could read /proc/interrupts, and on x86 UMWAIT or segment-limit tricks could expose the gap when EL0 is preempted to EL1.

macOS exposes no proc interface, Apple Silicon lacks UMWAIT and segment registers, and vendors now throttle architectural timers to blunt gap measurement.

Tide removes the timer entirely.

How Tide turns X18 into a heartbeat

ARM's AAPCS64 defines X18 as the platform register reserved for OS use, and Apple documents it as off-limits to apps.

Apple's Double Map hardening, introduced in 2017 for Meltdown-style isolation, keeps kernel mappings present but inaccessible in EL0 by reprogramming TTBR and TCR on context switch.

Two macros run before the kernel stack becomes accessible in the exception entry path.

Both macros use X18 as a scratch register, deterministically overwriting the user value on every interrupt.

X18 remains readable and writable from EL0, so user code can seed it, spin, and detect the overwrite.

Tide loops: set X18 to non-zero, increment a software counter, poll X18, record the counter when it flips to zero, reset and repeat.

Counter deltas become inter-interrupt intervals with no clock source.

How interrupts spread across Apple cores

Tide only sees its own core, so the researchers reverse-engineered the Apple Interrupt Controller to learn shared peripheral routing.

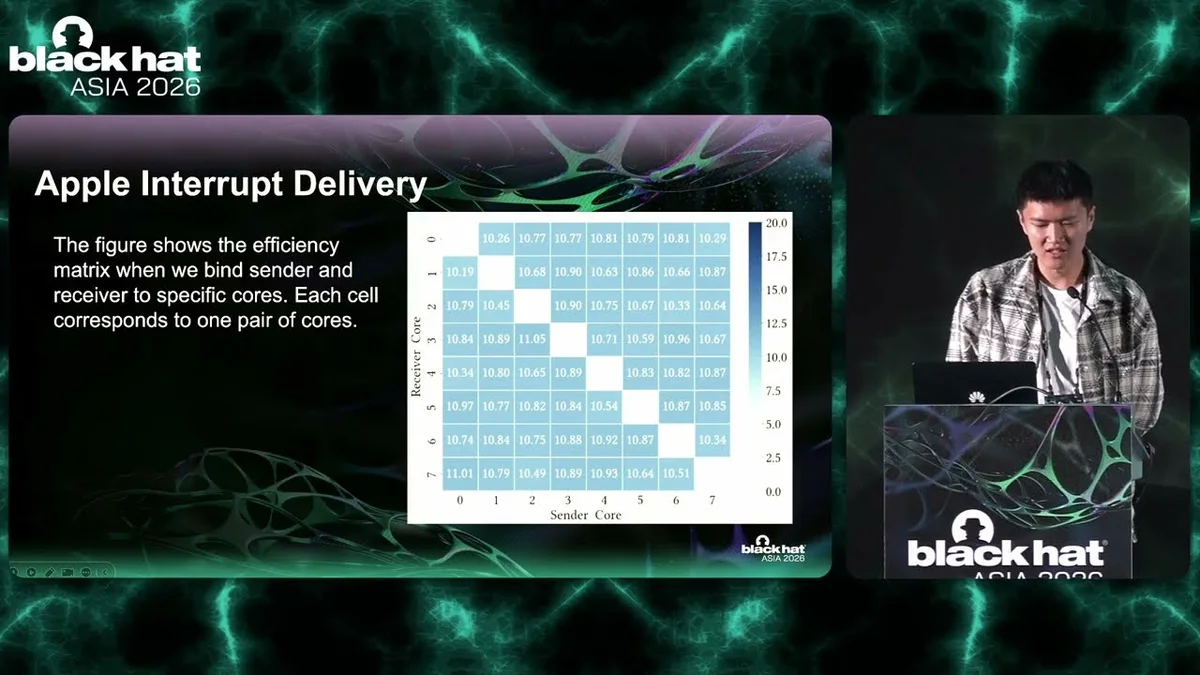
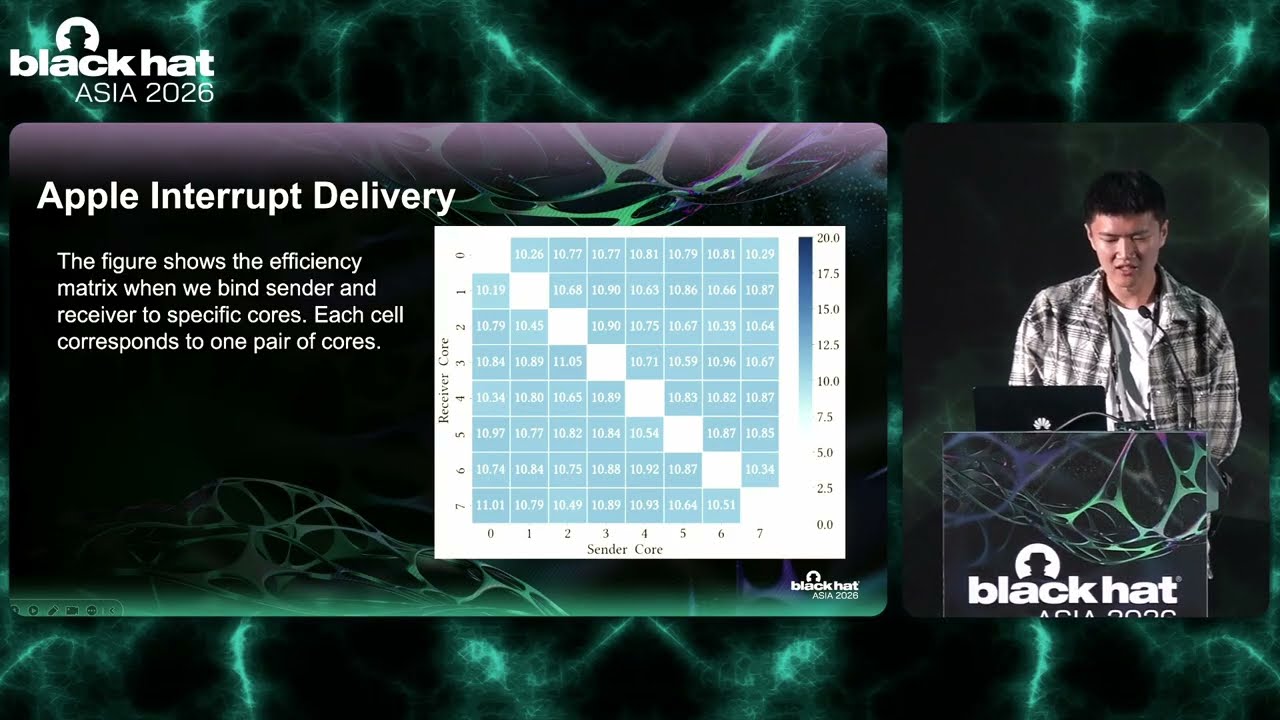
Using Commander, a kernel extension to pin threads to specific performance and efficiency cores, they measured efficiency as detected interrupts divided by sent network interrupts.

Sender and receiver pairs across all core combinations showed nearly uniform efficiency, unlike Linux's affinity-tied delivery.

Varying the active-core count showed busy cores received similar shares while idle cores received almost none.

Apple Silicon spreads shared peripheral interrupts uniformly across active cores only.

What an attacker can infer

Network activity drives network interrupts, and different pages produce different burst and gap patterns.

The team collected Tide traces for the Alexa Top 100 and trained an unmodified open-source CNN plus LSTM classifier on the interval sequences.

Closed-world identification hit 93.8% top-1 accuracy.

Open-world, with an extra class for outside-top-100, held at 91.5%.

Replacing the software counter with a fixed-frequency architectural timer gave nearly identical accuracy, confirming no dependence on frequency scaling.

On the top 20 YouTube videos the same pipeline reached 78.1% top-1 and 97.9% top-5 accuracy.

Disclosure and the mitigation gap

The authors disclosed separately to Apple's hardware security team and macOS security team.

Hardware security routed the report as a potential future hardening effort.

macOS security said findings may inform future platform enhancements but named no patch.

Both teams classified X18 events as out of scope under Apple's threat model.

A full OS fix would need to preserve the user X18 value before Double Map clobbers it, which is nontrivial because X18 must be overwritten before kernel mappings are valid, and Linux does not exhibit the same signal.

The tested user-space mitigation injected thousands of fake network interrupts per second at random intervals, cutting website fingerprinting to about 60% accuracy at roughly 10% overhead.

Why this matters for builders and buyers

Timer throttling, a go-to defense after a decade of cache and speculation leaks, does not block a deterministic register side effect.

Closed platforms hide procfs and x86-specific hooks but can still expose stable microarchitectural signals through OS hardening choices like Double Map.

For AI products that run browsing agents, meeting recorders or on-device inference on Macs, interrupt fingerprinting threatens session confidentiality even when traffic is encrypted.

Enterprises cannot patch X18 in software, so isolation must assume co-tenancy on active cores leaks coarse activity.

For founders, the takeaway mirrors recent confidential-computing debates: invest in independent hardware evaluation before assuming proprietary silicon is quiet.

Audit what your kernel clobbers in the entry path, not just what it exposes in APIs.

© 2026 StartupHub.ai. All rights reserved. You may not republish this article in full without a license. Search engines and AI research tools may crawl and summarize for reference. Bulk reproduction or model training requires a license. See our terms.

Watch

The videos behind the news, one flip at a time

The feed mixes the videos from our articles with startup demos and you flip through them like TV channels for free with no signup.

Daniel Singer

Written by

Daniel Singer

Editor, StartupHub.ai

Daniel Singer is the editor of StartupHub.ai, a technology expert and thought leader on AI and its applications across sectors, from fintech and healthcare to developer tooling and consumer software. He writes and tests the tools covered here thoroughly and regularly, and built StartupHub.ai to give founders, operators and buyers a clearer read on what they are actually being sold.