Cybersecurity

Coding Agents Security Failed 70 Times, Same Bugs

Palo Alto Networks researchers pwned 10 coding agents 70+ times with the same command and file-system bugs, and even OS sandboxes fell to symlink tricks.

StartupHub.ai Staff

By StartupHub.ai Staff, reviewed by Daniel Singer, Editor

4 min read

Visual TL;DR
Symlinks collapse sandboxesEffect
File system path tricks escape OS-level isolation completely
Agents self-policeDriver
Security still relies on the agent to restrict its own capabilities
From the article 9+ mentionsMost agents gate commands with a pre-approved list and ask for approval only when a command is not on it.
Prompt injection to RCEContext
Hidden prompts in files trigger same commands as direct user input
From the article 2 mentionsWhatever the agent will do for a user prompt it will also do for an injected prompt hidden in a file or issue, so the chain starts with injection and ends with RCE.
Allow lists bypassedDriver
Pre-approved command checks fail because injected prompts mimic approved usage
70+ flaws across 10 agentsOutcome
Palo Alto researchers pwned every tested coding agent identically
From the articleMore than 70 flaws across 10 coding agents fell to the same handful of bugs, according to BlackHat Asia 2026 talk Bad Vibes, and coding agents security still trusts the agent to police itself.
Agents self-policeDriver
Security still relies on the agent to restrict its own capabilities
From the article 9+ mentionsMost agents gate commands with a pre-approved list and ask for approval only when a command is not on it.
No novel exploits neededEffect
Same bugs work across every vendor without custom attack code
From the articleTwo vulnerability researchers from Palo Alto Networks (NASDAQ:PANW), Nila Shkenazi and Philip Zuckerman, walked the full kill chain from chat prompt to host takeover without a novel exploit.
Prompt injection to RCEContext
Hidden prompts in files trigger same commands as direct user input
From the article 2 mentionsWhatever the agent will do for a user prompt it will also do for an injected prompt hidden in a file or issue, so the chain starts with injection and ends with RCE.
Terminal tools execute commandsCore
From the article 2 mentionsThat assumption held in every agent they tested, because terminal tools are designed to run user supplied commands.
Allow lists bypassedDriver
Pre-approved command checks fail because injected prompts mimic approved usage
Symlinks collapse sandboxesEffect
File system path tricks escape OS-level isolation completely
70+ flaws across 10 agentsOutcome
Palo Alto researchers pwned every tested coding agent identically
From the articleMore than 70 flaws across 10 coding agents fell to the same handful of bugs, according to BlackHat Asia 2026 talk Bad Vibes, and coding agents security still trusts the agent to police itself.
Host takeover achievedOutcome
Kill chain completes from chat window to full machine control
From the articleTwo vulnerability researchers from Palo Alto Networks (NASDAQ:PANW), Nila Shkenazi and Philip Zuckerman, walked the full kill chain from chat prompt to host takeover without a novel exploit.
Contents(6)

More than 70 flaws across 10 coding agents fell to the same handful of bugs, according to BlackHat Asia 2026 talk Bad Vibes, and coding agents security still trusts the agent to police itself.

Coding Agents Security Failed 70 Times, Same Bugs - BlackHat
Coding Agents Security Failed 70 Times, Same Bugs, BlackHat

Two vulnerability researchers from Palo Alto Networks (NASDAQ:PANW), Nila Shkenazi and Philip Zuckerman, walked the full kill chain from chat prompt to host takeover without a novel exploit.


How does prompt injection become remote code execution?

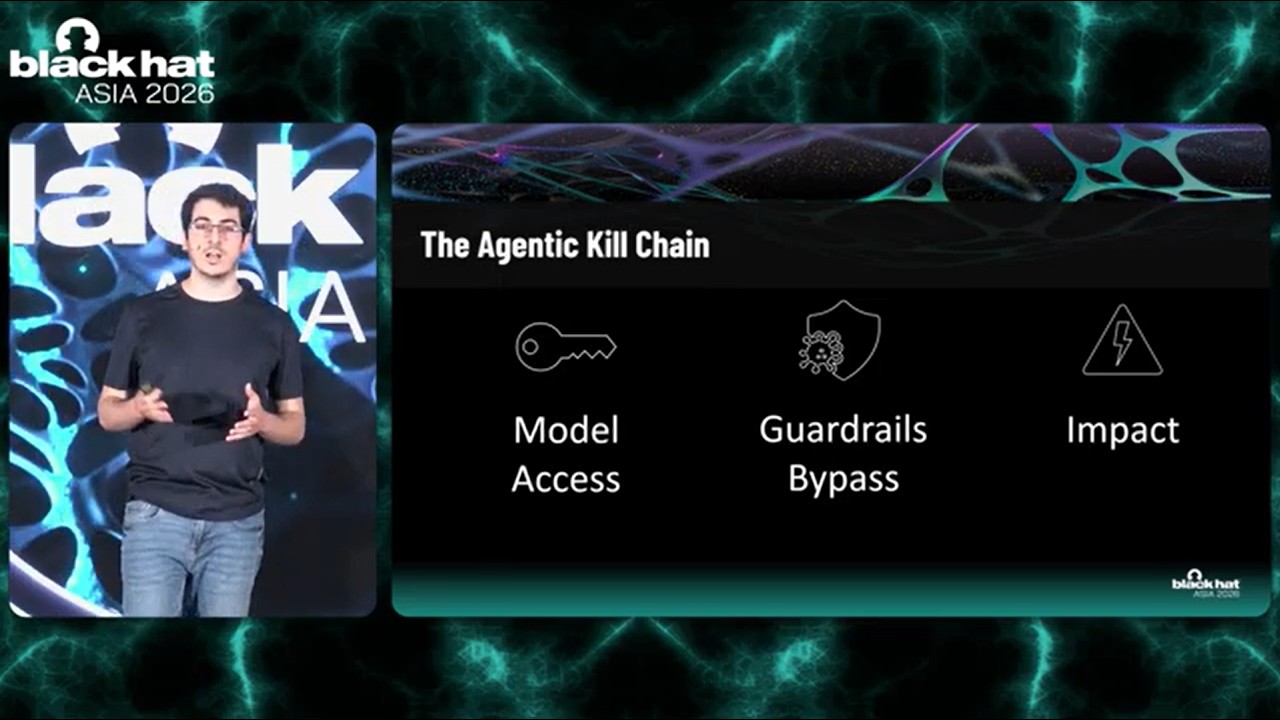
Their model is simple: model access plus guardrail bypass plus impact equals compromise, and they tested impact directly through the chat window.

Whatever the agent will do for a user prompt it will also do for an injected prompt hidden in a file or issue, so the chain starts with injection and ends with RCE.

That assumption held in every agent they tested, because terminal tools are designed to run user supplied commands.

Why did allow lists and command checks fail everywhere?

Most agents gate commands with a pre-approved list and ask for approval only when a command is not on it.

Compound commands broke the gate, because if dir was allowed but calc was not, dir and calc still ran in several agents.

Alphabet Inc. (NASDAQ:GOOGL) Gemini CLI tried to fix this by parsing PowerShell into an AST and checking command nodes, but a bug forced it to launch cmd instead and reduced the check to prefix matching.

How did file system checks fail the same way?

Agents must write inside the workspace, but that workspace contains sensitive configs like MCP server definitions, permission files, and git config that control future execution.

Path checks used exact suffix matching, so MCP.json and MCP.JSON were treated as different on case-insensitive Windows and macOS.

NTFS quirks made it worse, with short names like agent~1 and alternate data streams like file:$DATA letting the agent write to .cursor or .claude folders without triggering the deny.

How did the same tricks collapse the sandboxes?

Big vendors moved enforcement to the OS with namespace mounts on Linux and Seatbelt policies on macOS that deny writes to sensitive paths and allow writes to the workspace.

Those policies still failed on semantics, because writing to whatever.json then moving it to agent settings.json never matched a deny rule on the target path.

Symlink handling produced two more escapes, one that poisoned the next policy by linking temp to root and one classic time of check to time of use race where link flipped between a real file and a symlink outside the workspace.

Why does this repeat across every vendor?

Command line parsing cannot enumerate malicious behavior reliably, a lesson endpoint detection teams learned years ago, and file system semantics differ by OS in ways model-level prompts never see.

The same week, separate Black Hat USA research showed Gemini CLI and Claude Code flaws where harness code marked a value safe and later code executed it with higher privilege, leading to CVE-2026-12537 and CVE-2026-54316.

Palo Alto Networks filed 26 reports on command injection with 7 CVEs, 43 on file system with 9 CVEs, and 13 on sandbox escapes, totaling more than 81 reports and about 18 CVEs to date.

What should founders and teams do now?

Do not count CVEs to pick the most secure agent, because disclosure speed varies and some vendors fixed silently without CVEs while others argue prompt injection to RCE is not a boundary.

Run agents in an ephemeral container or VM you can nuke after each session, and treat WSL as no isolation since it shares the Windows user filesystem and can write to startup folders.

The talk closed with a blunt trade off: vendors are choosing between autonomy and endless approval prompts, and until OS enforcement covers file tools as well as terminals, that choice stays with you.

Sources

Get the free daily brief every morning

Every morning the day's AI news, new AI startups and new funding rounds. Free and takes a few minutes to read, unsubscribe at any time.

Join 64,000 other subscribers.

TopicsPalo Alto NetworksBlack Hat AsiaBad VibesGemini CLIClaude CodeCursorNASDAQ:PANWNASDAQ:GOOGL

StartupHub.ai Staff

Written by

StartupHub.ai Staff

Editorial team

The staff writers of StartupHub.ai, ranging from investment analysts to avid AI tool users, early adopters and critical enthusiasts. Backgrounds span engineering, business and the arts. We hold every piece to rigorous standards of research and review.

Daniel Singer

Written by

Daniel Singer

Editor, reviewed this article

Daniel Singer is an AI expert who has been writing about, covering and building AI technology since 2018.

Test your Agent Readiness now

Paste your website. How well ChatGPT, Claude and the other agents can read and use a site, in about a minute.

Watch

The videos behind the news, one flip at a time

The feed mixes the videos from our articles with startup demos and you flip through them like TV channels for free with no signup.