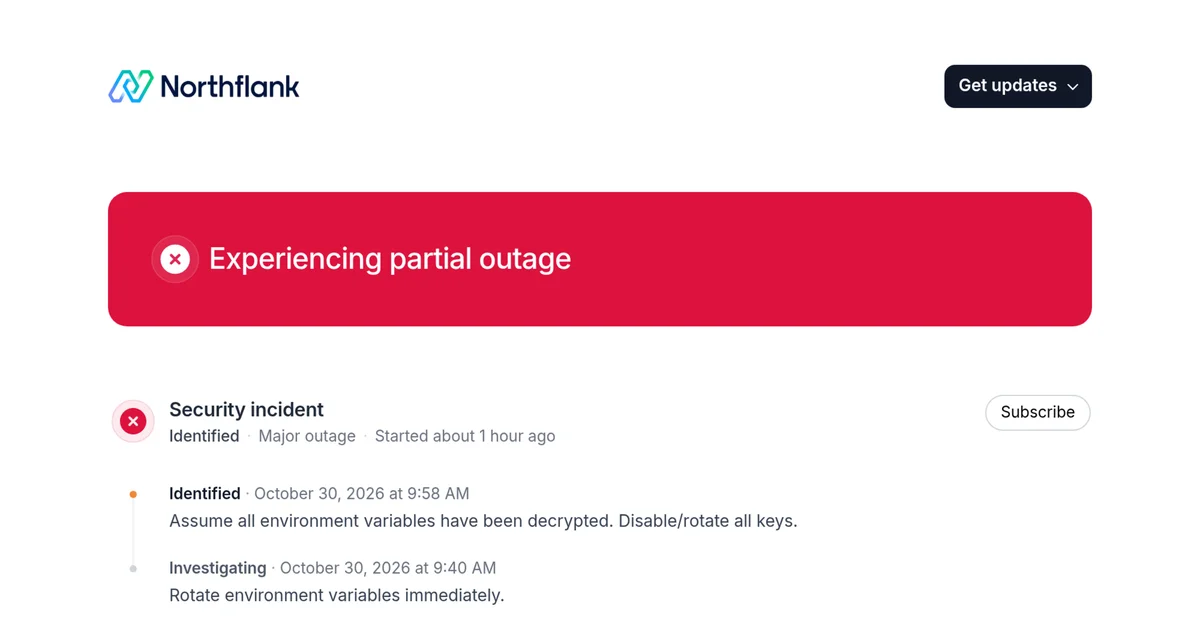
Northflank says assume all environment variables have been decrypted and rotate every secret now.
The instruction came in a terse identified update, and it leaves engineering teams with immediate work. The Northflank status page says the blast radius includes workload secrets, secret groups and global secrets, and it tells teams to revoke credentials with their issuing providers, generate replacements, and update workloads. For teams that exposed Postgres and MongoDB addons to the public internet, the guidance is to disable that access and rotate addon secrets, a step Northflank says it has now enabled for all users.
Northflank said users have reported unauthorized use of AI API keys supplied to the platform, and it asked teams to review provider usage and billing logs for unexpected activity. Northflank said those reports may be consistent with a broader pattern of attacks targeting AI credentials and pointed to similar IP addresses documented in Wiz's Black October report. Wiz, the cloud security vendor that issued the initial threat alert at 11:43 UTC, was later brought in for CIRT support, per the timeline Northflank published.
The timeline itself is spare. Northflank says its engineers reviewed the Wiz alert at 11:44 UTC, deployed an initial network policy patch at 12:02 UTC, then shipped additional patches through the afternoon. At 7:28 PM UTC, Northflank said its investigation was ongoing and it had no further confirmed findings to share. Users, meanwhile, are already confirming active abuse of AI keys, according to Northflank. That gap between confirmed findings and reported abuse is the tension in the disclosure.
Independent coverage described the event as a breach spanning core platform components, with Networking, Certificates, Services, Addons, Jobs, Builds, and Logs and Metrics all listed under major outage, according to daily.dev. Northflank lists its application, API, marketing site and documentation as operational while the platform remains degraded. In its most recent update, Northflank said it has enabled audit logs for all customers, including free users.
The daily brief
Get the free daily brief with the day's AI news, new AI startups and funding rounds every morning.
Join 12,007 subscribers.
No fix is detailed beyond network policy changes, and Northflank has not described how environment variables were decrypted, whether secrets were exfiltrated, or how long exposure lasted. For teams that relied on Northflank to hold AI provider keys and database credentials in one place, the workflow change is immediate, rotate everything, reissue external keys, redeploy workloads, and pay for any AI usage burned by someone else. The question Northflank has not answered is what an attacker actually obtained and how.