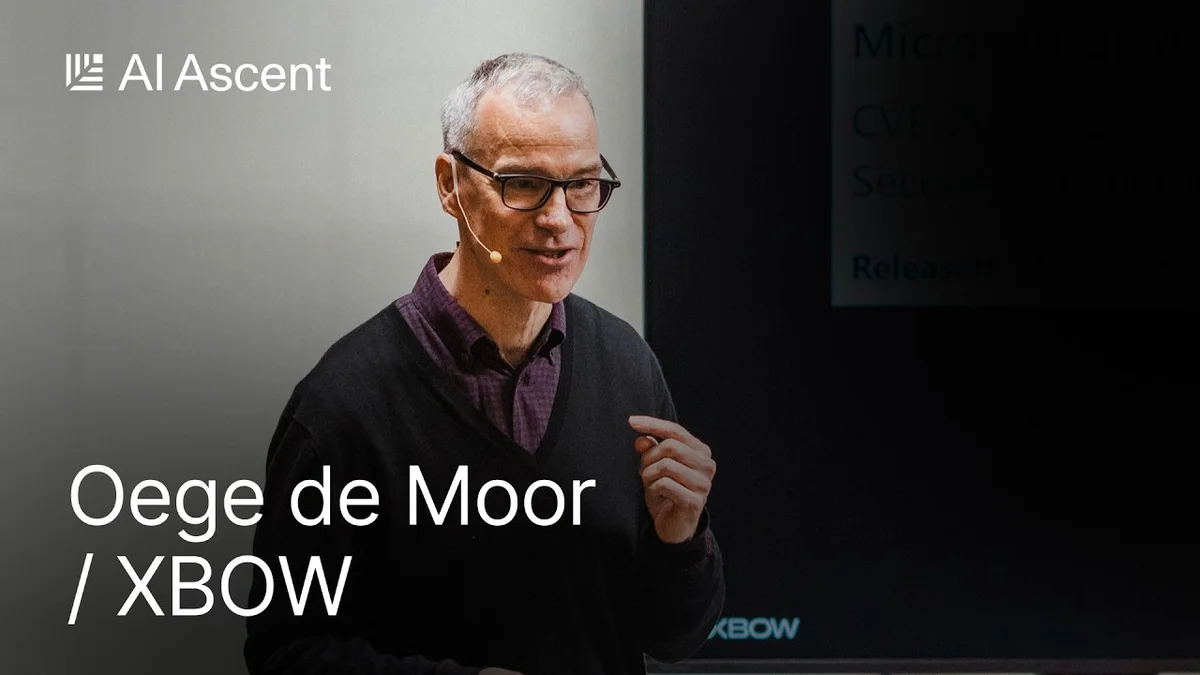
In a compelling presentation, Oege de Moor, associated with XBOW, offered a glimpse into the emerging world of autonomous AI hackers. De Moor, a prominent figure in the cybersecurity research community, discussed how artificial intelligence is transforming the landscape of vulnerability discovery and exploitation. The talk, aimed at a knowledgeable audience, highlighted the increasing sophistication and autonomy of AI agents in identifying and leveraging software weaknesses, drawing parallels to historical shifts in warfare and technological advancement.
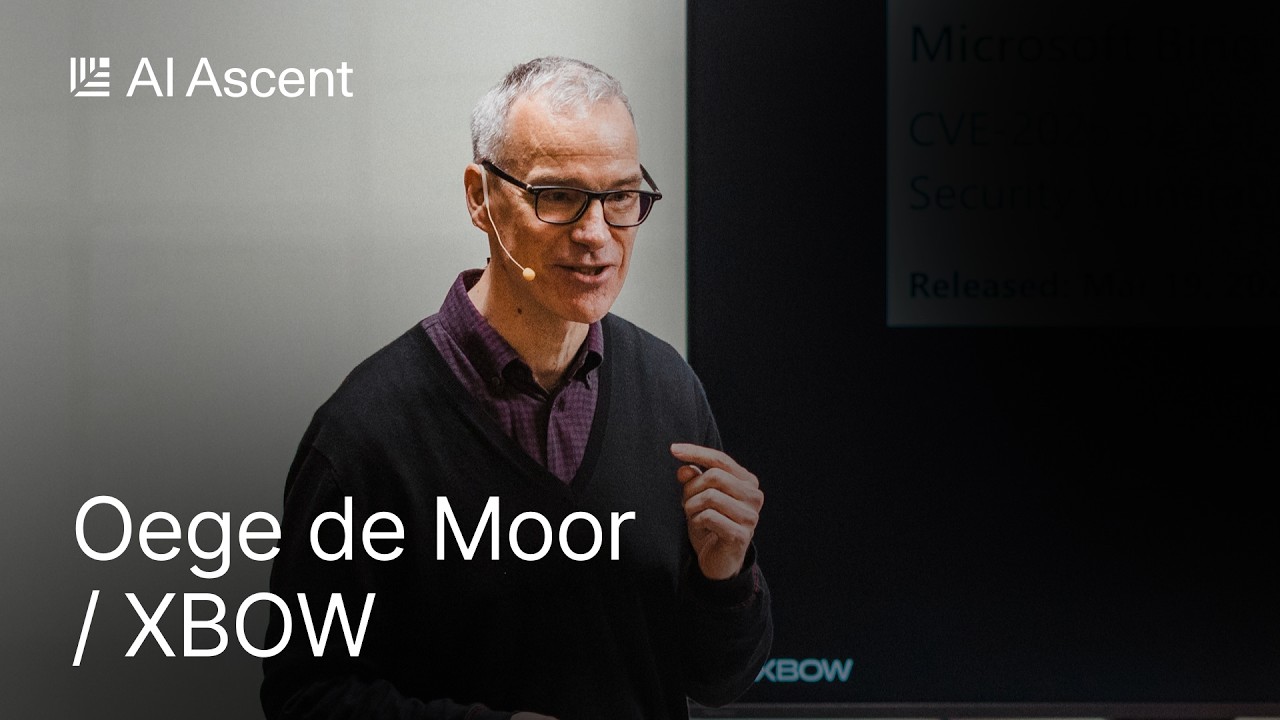
Who is Oege de Moor and XBOW?
Oege de Moor is presented as a key figure in the field of AI-driven cybersecurity, specifically within the context of autonomous hacking capabilities. While the provided information does not detail de Moor's specific background beyond his association with XBOW, the context of the presentation suggests expertise in AI research and application, particularly in security. XBOW, the entity de Moor represents, appears to be at the forefront of developing and utilizing AI agents for cybersecurity tasks, including vulnerability detection and exploitation.
The Rise of Autonomous AI Hackers
De Moor's presentation began by framing the current cybersecurity situation as a battleground where AI is increasingly playing a significant role. He drew a historical analogy to the Battle of Nagashino in 1575, where Oda Nobunaga's army, equipped with advanced firearms, defeated the cavalry-centric forces of the Takeda clan. This analogy serves to illustrate how technological superiority, specifically the adoption of new tools, can dramatically shift the balance of power. De Moor posited that autonomous AI agents are the new 'firearms' in the cybersecurity realm, capable of performing complex tasks without direct human oversight.
He detailed how human hackers have historically used AI as an assistant, but the trend is now shifting towards AI performing the entire process autonomously. This includes reconnaissance, identifying vulnerabilities, and executing exploits. De Moor highlighted a specific example of a Microsoft Bing Images remote code execution vulnerability (CVE-2026-32191) discovered by an AI, which required only a URL as input to find and exploit. This demonstration underscored the efficiency and autonomy that AI agents are achieving.
The Performance of AI Models in Security
A significant portion of the presentation focused on the rapid advancements in AI model performance, particularly in the context of security tasks. De Moor presented data showcasing the performance of various AI models, including 'Sonnet,' 'Gemini,' 'Alloy,' and 'GPT' variants, over time. The graph displayed a clear trend of increasing 'Solver Success Rate' from August 2025 to the present. Notably, the gap between open-weight models and proprietary models in these benchmarks is shrinking rapidly. De Moor projected that within 6-9 months, open-weight models would catch up to proprietary ones, emphasizing that this timeline represents a critical deadline for the cybersecurity community to adapt.