

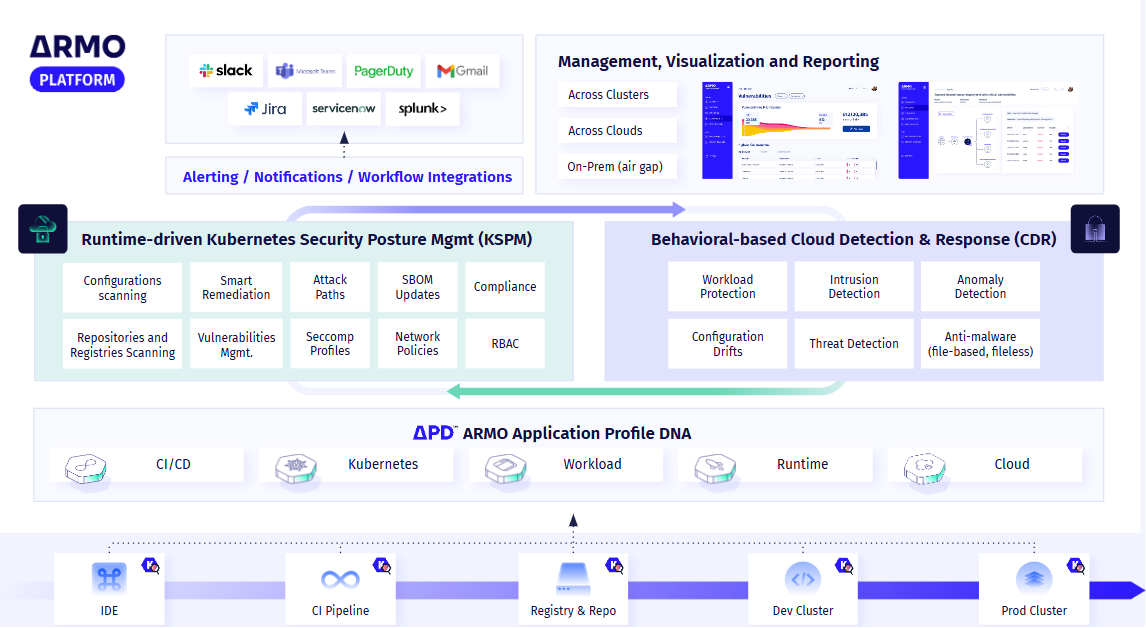
ARMO, the Cloud security and workload protection innovator and creator of Kubescape, announced today the launch of its new ARMO Cloud Detection & Response solution, providing robust security for workloads.
The new offering addresses the residual threats that may persist during runtime, even after thorough scanning during development and deployment. The solution builds on Kubescape's open-source threat detection capabilities by adding observed application behavior with context from Kubernetes, cloud environment, security policies, and workload characteristics. This creates a unique Application Profile DNA (APDTM) that serves as the baseline for detecting anomalies, malicious activities, and malware in real-time.
ARMO's approach focuses on providing actionable results while reducing false positives, without impacting application functionality. This approach leads to more secure applications while mitigating alert fatigue for security teams.
By utilizing Kubescape, ARMO Platform boosts workload protection within Kubernetes clusters by providing runtime threat detection and response capabilities. Using an eBPF-based runtime sensor to determine expected application behavior, Kubescape establishes a baseline and will then detect and flag any deviations or suspicious behavior, leading to enhanced workload protection. This technology focuses on reducing false positives and maintaining a low resource footprint, reducing operating costs by up to 60% compared to traditional runtime agents.
"Legacy Endpoint Detection & Response solutions have struggled to keep up with the visibility and context challenges posed by modern containerized and cloud-native microservices architectures running on Kubernetes, necessitating the evolution to Cloud Detection and Response," said Ben Hirschberg, CTO and co-founder of ARMO, and core maintainer of Kubescape.