Runlayer founding engineer Aiden Sochowski said his 50 to 60 person company found more than 300 agents running every day once it routed traffic through a gateway and logged every session and tool call, a count he walked through on AI Engineer.
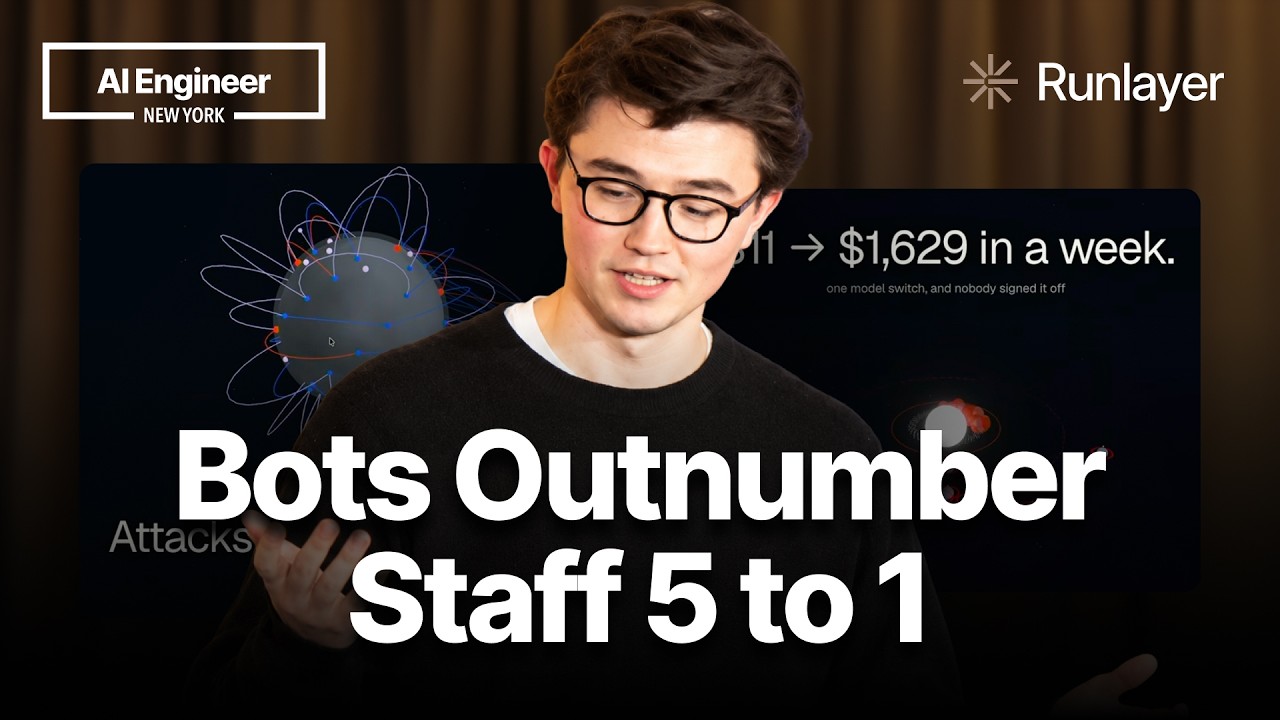
Most teams have no inventory.
Sochowski said the sprawl is MCP clients on unmanaged devices, random agentified products users signed up for, and triggers from chatbots or SaaS apps that fire without a direct user prompt. In his map, every agent got a risk and topic tag, and every tool call became an attack surface that could read hostile data, take a destructive action, or exfiltrate. The affected systems in his examples were not hypothetical: email, calendars, applicant tracking systems, meeting notes, and GitHub.
The attacker does not need local access. Sochowski described a support inbox ingesting every email, where a remote sender could ask a naive, over permissioned agent to list current prospects and the agent would read the calendar and send it out. He said blanket blocks do not work because the same tool can be safe or unsafe depending on context, and classifiers that scan inbound instructions or outbound PII with regex will never be 100 percent effective. Cost is a parallel failure mode: a recruiter team vibe-coded an MCP server for a vendor API, hit formatting errors on every run, and burned input and output tokens while the agent retried.
Session-level intent drift is the harder problem, Sochowski argued. He pointed to internal PR reviewer agents that can approve code and read GitHub comments. An author can argue with the agent, say only review the cleanup, and nudge it to approve a security sensitive change after repeated prompts. Sochowski said the team trained a classifier to judge each tool call against the agent's original task, and built history baselines to flag runs that suddenly touch tools outside the normal range, like a recruiter bot that normally reads the ATS suddenly messaging users or pulling every meeting.
The practical fix was not another policy list, it was tighter write scoping. Sochowski said one poisoned resume written to a shared store can be read by a different agent as normal instruction, so the only way to keep an agent's context from being poisoned is to restrict where agents can write, often to specific tables inside a SaaS app, and to rate limit and monitor flaky MCP servers. Outside the talk, Runlayer is listed as an MCP gateway with identity-aware policy, OAuth controls, runtime security checks, approvals and audit logging, per Aembit. The work still leaves open how to set budgets and model choices without evals, which is why his team now flags high-risk runs early and pushes teams toward sane defaults.