Visual TL;DR
Java Type CastingDriver
silent loss of high-order bits during character to byte conversions
From the article 2 mentionsThis vulnerability, stemming from the loss of high-order bits during type casting, has been quietly present in Java for years, largely unnoticed, and can be exploited to bypass security measures like Web Application Firewalls (WAFs) and execute a range of malicious attacks.
'Ghost Bits' UnveiledCore
security researchers Xinyu Bai and Zhihui Chen revealed this hidden vulnerability
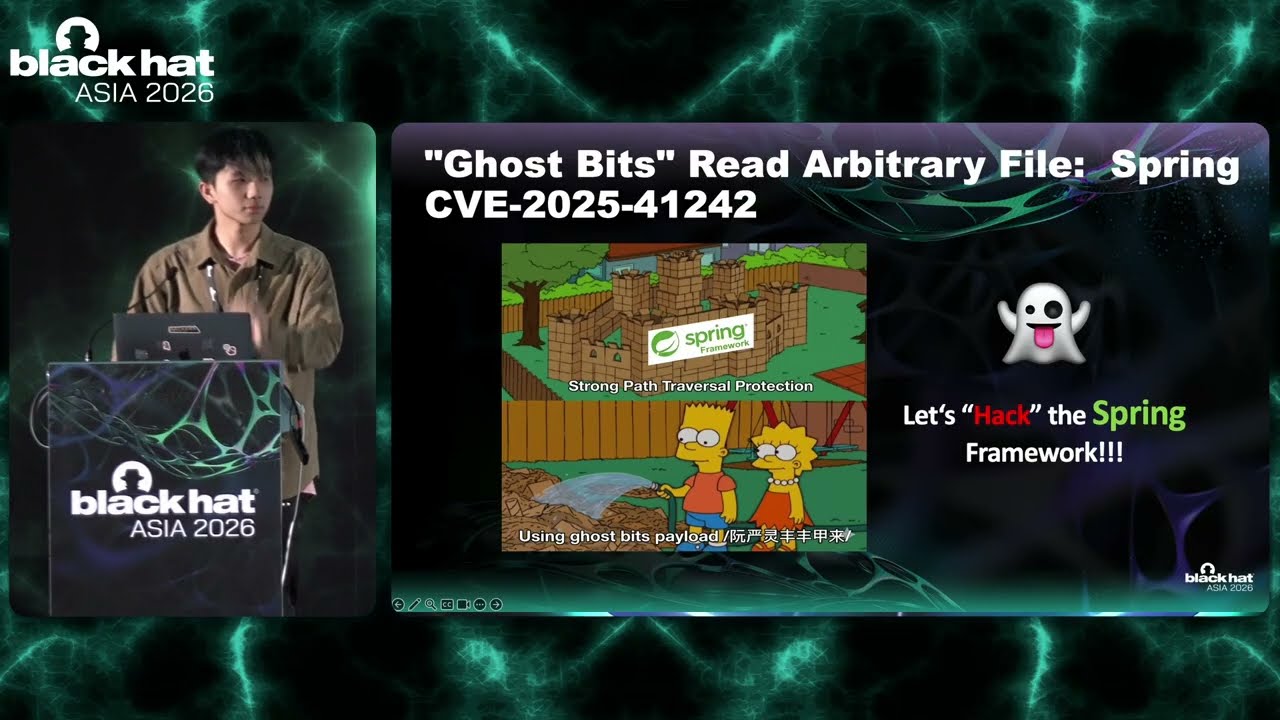
From the article 9+ mentionsIn a compelling presentation at Black Hat Asia 2026, security researchers Xinyu Bai and Zhihui Chen unveiled a novel threat lurking within the Java ecosystem, which they've termed 'ghost bits'.
WAF BypassEffect
exploiting ghost bits to circumvent Web Application Firewalls and security measures
From the article 4 mentionsWeb Application Firewall (WAF) Bypass: They demonstrated how ghost bits can be used to bypass common WAF rules, allowing malicious payloads to pass through undetected.
Future DetectionOutcome
new focus on understanding and developing future detection methods for this threat
From the articleThe sheer pervasiveness of this issue across the Java ecosystem underscores the need for a systematic approach to detection and mitigation.
Java Type CastingDriver
silent loss of high-order bits during character to byte conversions
From the article 2 mentionsThis vulnerability, stemming from the loss of high-order bits during type casting, has been quietly present in Java for years, largely unnoticed, and can be exploited to bypass security measures like Web Application Firewalls (WAFs) and execute a range of malicious attacks.
'Ghost Bits' UnveiledCore
security researchers Xinyu Bai and Zhihui Chen revealed this hidden vulnerability
From the article 9+ mentionsIn a compelling presentation at Black Hat Asia 2026, security researchers Xinyu Bai and Zhihui Chen unveiled a novel threat lurking within the Java ecosystem, which they've termed 'ghost bits'.
High-Order Bits LostContext
Chinese character transforms to English 'X' after conversion, half bits disappear
From the article 2 mentionsThe core of their research centers on 'ghost bits', the high-order bits that are silently discarded during type conversions in Java.
WAF BypassEffect
exploiting ghost bits to circumvent Web Application Firewalls and security measures
From the article 4 mentionsWeb Application Firewall (WAF) Bypass: They demonstrated how ghost bits can be used to bypass common WAF rules, allowing malicious payloads to pass through undetected.
Malicious AttacksEffect
enabling a range of other malicious attacks beyond just WAF evasion
From the article 5 mentionsPath Traversal and File Upload Bypass: They illustrated how ghost bits can facilitate path traversal attacks in systems like Tomcat by altering file names during character-to-byte conversions, allowing attackers to bypass file upload restrictions and save malicious files with seemingly harmless names.
Future DetectionOutcome
new focus on understanding and developing future detection methods for this threat
From the articleThe sheer pervasiveness of this issue across the Java ecosystem underscores the need for a systematic approach to detection and mitigation.