


The cybersecurity landscape is set to become significantly more volatile by 2026, according to the latest IBM X-Force Threat Intelligence Index. The report highlights an alarming surge in vulnerability exploitation, supply chain compromises, and ransomware attacks, exacerbated by the proliferation of AI and evolving attacker tactics, techniques, and procedures (TTPs).
X-Force analysts observed a 44% rise in incidents stemming from vulnerability exploitation, with nearly 40,000 new vulnerabilities reported, a 13,000 increase year-over-year. Compounding this, 56% of tracked vulnerabilities allowed exploitation without authentication. This critical flaw enables attackers to bypass traditional defenses like phishing, passwords, and multi-factor authentication, leaving minimal forensic trace and indicating systems often remain insecure by design.
The report also details a near fourfold increase in supply chain and third-party compromises over the last five years. Attackers are increasingly targeting software development and deployment ecosystems, particularly through SaaS integrations. Introducing vulnerabilities at this stage creates a 'house of cards' scenario, where a single compromised component can destabilize an entire system.
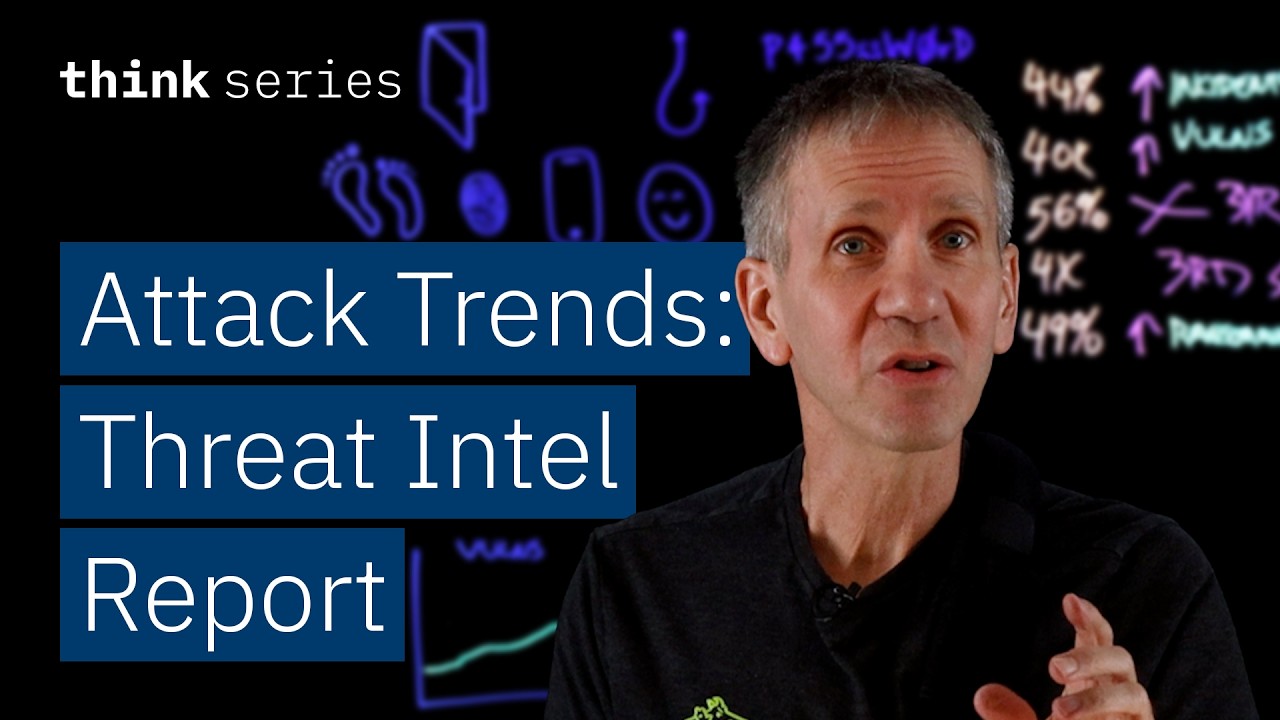
Ransomware groups surged by 49% in the past year, driven by smaller, more transient operations. The advent of AI and Ransomware-as-a-Service (RaaS) tools has dramatically lowered the barrier to entry, allowing attackers to "set it and forget it" with automated target identification and exploit deployment. This decentralization makes threat actors harder to trace and combat.
A notable trend is the blurring of TTPs between nation-state actors and financially motivated cybercriminals. Previously distinct attack methodologies are converging, with groups like North Korean state actors now employing info-stealers, malware designed to pilfer passwords and secrets, a tactic once predominantly used by cybercriminals.