The burgeoning field of AI agents, capable of autonomous action based on high-level goals, necessitates a robust governance framework to ensure reliability and alignment with human intentions. Amanda Winkles, an AI/MLOps Technical Specialist in IBM's Financial Services Market, recently elucidated a comprehensive, five-pillar approach to agentic AI governance. Her presentation underscored the critical need for structured oversight, drawing a vivid analogy of a driverless car endlessly circling a parking lot, highlighting the potential for unintended and undesirable autonomous behavior if not properly managed.
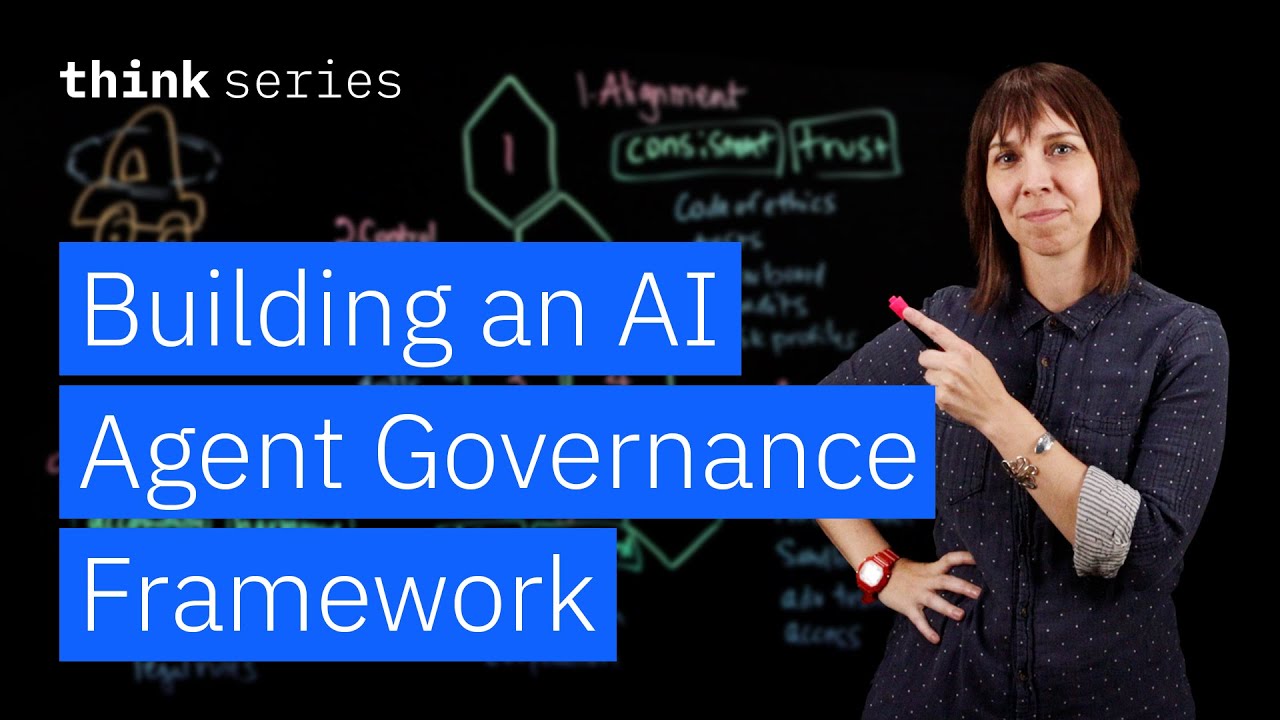
Winkles articulated that AI agents, powered by Large Language Models (LLMs), operate by determining their own methods to achieve user-defined objectives, rather than executing explicit, step-by-step instructions. This inherent autonomy, while powerful, introduces complexities that traditional AI governance models may not fully address. The IBM framework, therefore, focuses on specific policies, processes, and controls for each of its five foundational pillars: Alignment, Control, Visibility, Security, and Societal Integration.
The first pillar, **Alignment**, is paramount, establishing trust that agents will consistently behave in accordance with organizational values and intentions. To achieve this, organizations should institute a clear code of ethics, embedding it within every agent development project. Crucially, metrics and tests must be defined to detect "goal drift," running both pre-deployment and regularly thereafter. An independent governance review board is essential for ensuring regulatory compliance, such as with the EU AI Act, and for approving deployments based on test results. Finally, automated audits check agent outputs against specifications, while risk profiles, informed by organizational risk preferences, are encoded into agent parameters during development.
The second pillar, **Control**, ensures agents operate within predefined boundaries. An action authorization policy is vital, delineating which actions an agent can undertake autonomously versus those requiring human intervention. This human-in-the-loop mechanism is a critical safeguard. Organizations should also maintain a tool catalog, listing approved tools (databases, APIs, plugins) for agent use, along with lineage tracking to understand which agents employ which tools. To prepare for contingencies, regular "shutdown and rollback drills" should be conducted, simulating agent misbehavior to test intervention speeds and recovery procedures. A kill switch mechanism, offering both soft stops for orderly shutdowns and hard stops for emergency termination at the orchestration layer, provides ultimate recourse. Comprehensive activity logs, recording every agent action, input, and output, enable future modification or reversal if necessary.
**Visibility**, the third pillar, focuses on making agent actions observable and understandable. This involves assigning unique agent IDs to trace behavior across various environments. Furthermore, a well-defined incident investigation protocol, with clear steps from log retrieval to root cause analysis, is indispensable for responding to unexpected agent actions. Continuous testing for multi-agent interactions is also emphasized to evaluate cooperation capabilities, detecting coordination failures before they impact users.