

Privado’s 2024 State of Website Privacy Report revealed that 75% of the 100 most visited websites in the US and Europe are non-compliant with current privacy regulations.
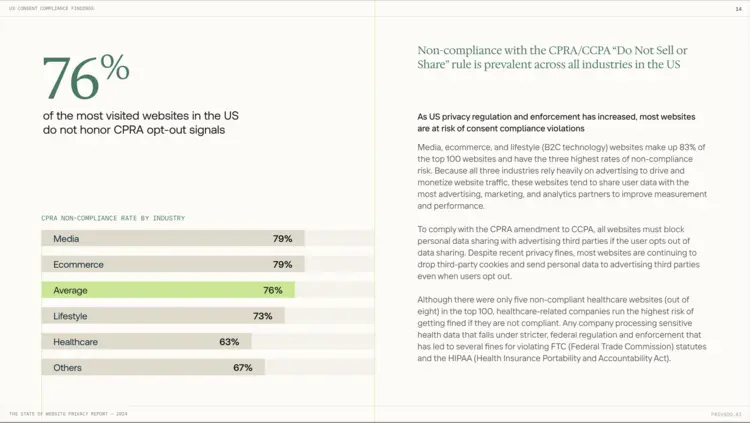
In Europe, 74% of top websites fail to meet the GDPR’s opt-in consent standards, while in the US, 76% of popular sites are not adhering to opt-out consent requirements under the California Privacy Rights Act (CPRA). Compliance risk levels were found to be three times higher in the US than in Europe.
The report, based on Privado’s consent monitoring data from September 2024, highlights significant compliance challenges despite the widespread use of cookie banners. Many of these banners are misconfigured, failing to keep up with the rapidly changing landscape of marketing technologies. Privado’s findings underscore the growing gap between regulatory requirements and actual website practices, with most websites unable to effectively manage evolving consent requirements.
Recent enforcement trends show increased fines for consent non-compliance, adding legal and reputational risk for businesses. Since 2018, six of the twenty largest GDPR fines, including Amazon’s $888 million fine, have been issued due to consent violations. In the US, CPRA and federal regulations like HIPAA are prompting more companies to evaluate their consent management practices, as non-compliance fines become more common.
According to Privado, the US and Europe’s leading websites share user data with an average of 17 third-party advertisers in the US and six in Europe. This extensive data sharing raises compliance risks, as many privacy teams lack the tools to track which third parties access user data or if they are following consent protocols.