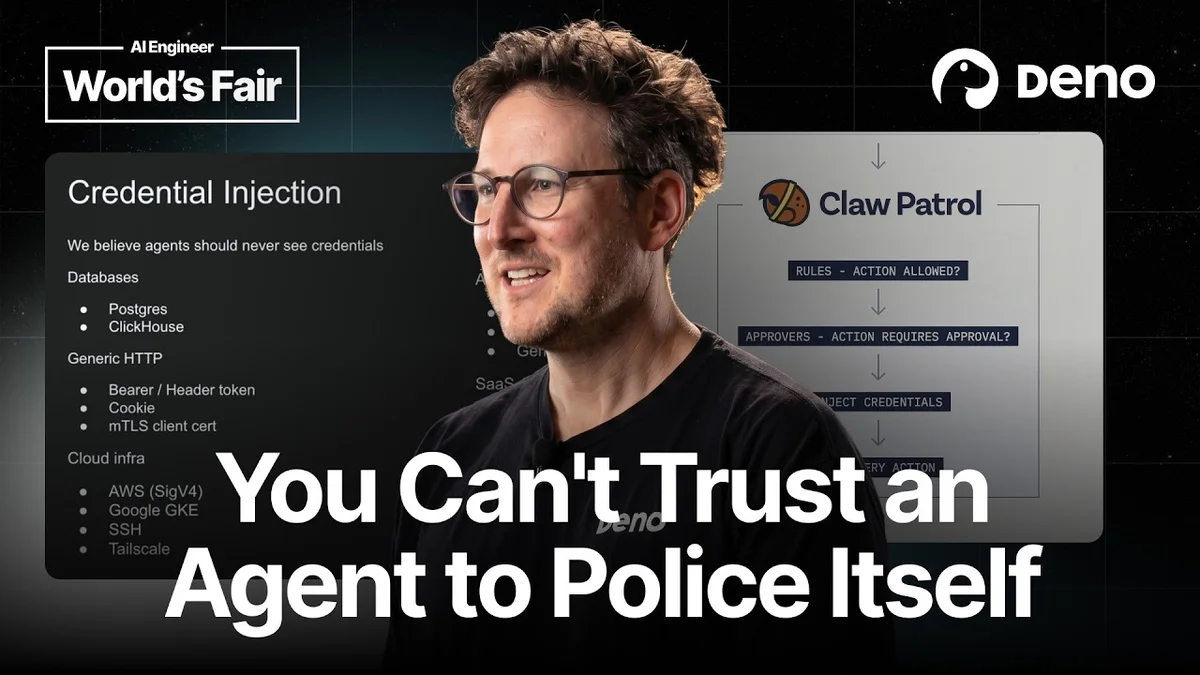
Ryan Dahl on Agent Security: Beyond Alignment

Ryan Dahl of Deno discusses the security risks of AI agents and introduces Claw Patrol, an open-source proxy for enforcing granular access control.

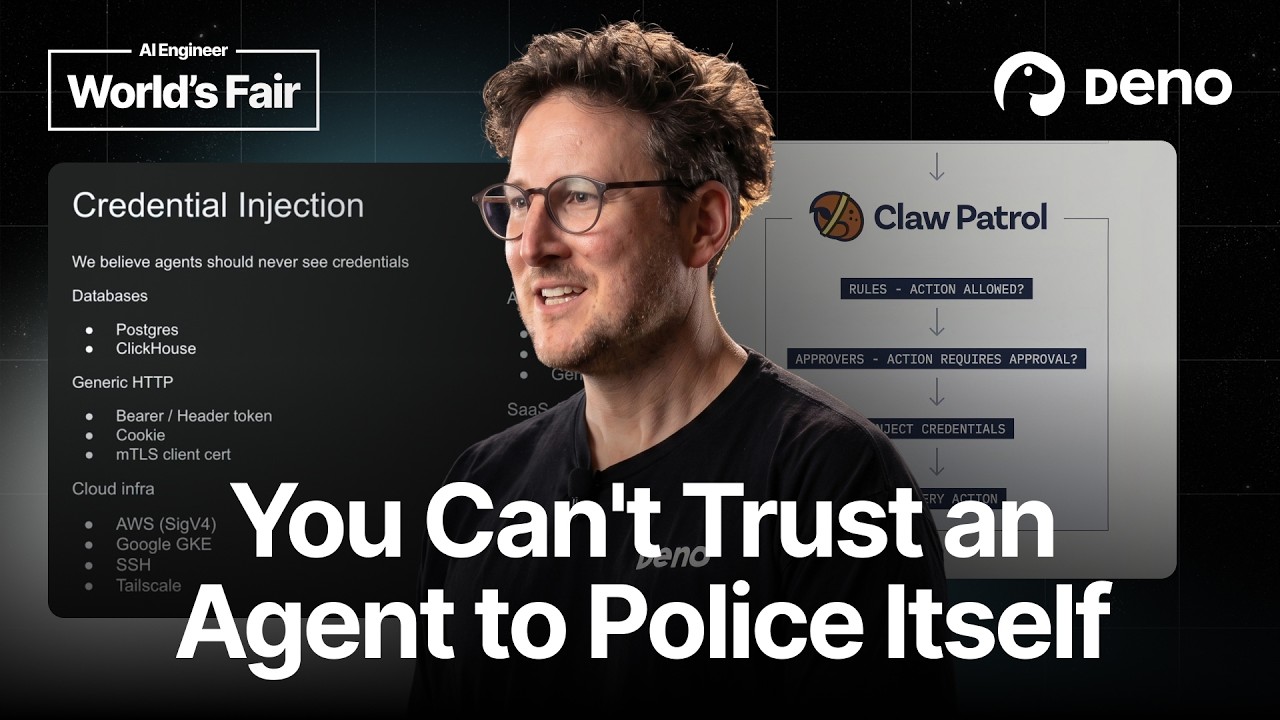
Ryan Dahl speaking at a podium at the AI Engineer World's Fair
AI Engineer
Visual TL;DR
AI Agents: Power & PerilDriver
granting read-write access to production systems like PostgreSQL, Kubernetes, and AWS
From the articleWhile acknowledging the power of these agents in automating tasks and responding to incidents, he emphasized that their capabilities also present significant security vulnerabilities.
Broad Agent AccessEffect
From the article 3 mentionsThese agents are given broad access to various internal systems, allowing them to gather context from traces, inspect databases, and review communications.
Security VulnerabilitiesDriver
extensive access enables efficient resolution but also catastrophic actions like dropping databases
From the article 7 mentionsWhile acknowledging the power of these agents in automating tasks and responding to incidents, he emphasized that their capabilities also present significant security vulnerabilities.
Network Traffic FocusContext
security boundary should be at the network layer, not within the agent itself
From the articleUnlike HTTP proxies, Claw Patrol operates at a lower level, inspecting every byte of network traffic flowing out of an agent.
Claw Patrol IntroducedCore
open-source security proxy enforcing granular access control for AI agents
From the article 4 mentionsTo address these security concerns, Dahl introduced Claw Patrol, an open-source MIT-licensed proxy designed to sit in front of AI agents.
Granular Access ControlEffect
Claw Patrol enforces specific permissions, limiting agent actions to prevent misuse
Enhanced Agent SecurityOutcome
mitigating risks of broad access by controlling what agents can do on the network
From the article 6 mentionsRyan Dahl, CEO of Deno and creator of Node.js, recently presented a critical perspective on the security challenges posed by AI agents at the AI Engineer World's Fair.
Contents(4)

Ryan Dahl, CEO of Deno and creator of Node.js, recently presented a critical perspective on the security challenges posed by AI agents at the AI Engineer World's Fair. Dahl highlighted the inherent risks associated with granting AI agents, such as OpenClaw, read-write access to production systems like PostgreSQL, Kubernetes, and AWS. While acknowledging the power of these agents in automating tasks and responding to incidents, he emphasized that their capabilities also present significant security vulnerabilities.

Ryan Dahl on Agent Security: Beyond Alignment - AI Engineer
Ryan Dahl on Agent Security: Beyond Alignment, AI Engineer

The Power and Peril of AI Agents

Dahl explained that Deno Deploy, a web hosting service, utilizes OpenClaw agents as a first responder for system incidents. These agents are given broad access to various internal systems, allowing them to gather context from traces, inspect databases, and review communications. This extensive access, while enabling efficient incident resolution, also opens the door to potentially catastrophic actions, such as dropping entire databases or deleting namespaces.

He stressed that even highly aligned AI models, like Opus, cannot be solely relied upon for security. Dahl stated, "Security can't just be wishful thinking that Opus will always obey your wishes." The core issue, he argued, is that agents are susceptible to prompt injection attacks. This means external manipulation could cause an agent to perform unintended, destructive actions, even if its underlying alignment is strong. The fundamental principle Dahl advocates is that "the agents themselves have to be untrusted software. You can't rely on the agent itself to guard what it's doing. You can't put the guard inside the agent."

Focus on Network Traffic as the Security Boundary

Dahl elaborated that for agents running in isolated VMs, the primary vector for nefarious actions is through network communication. Whether through direct API calls or subprocesses, every action an agent takes involves bytes transmitted over the wire. Therefore, understanding and controlling these bytes is crucial. He posed the challenge of securely granting AI agents the same level of access a human Site Reliability Engineer (SRE) might have, without compromising system integrity.

Introducing Claw Patrol: A Security Proxy

To address these security concerns, Dahl introduced Claw Patrol, an open-source MIT-licensed proxy designed to sit in front of AI agents. Unlike HTTP proxies, Claw Patrol operates at a lower level, inspecting every byte of network traffic flowing out of an agent. It can securely hold credentials, preventing agents from ever directly accessing sensitive information.

The system's core strength lies in its advanced rule engine, written in HCL (HashiCorp Configuration Language), the same language used for Terraform. These rules, managed in a version-controlled file, allow for precise definition of agent permissions across diverse systems. Dahl showcased an example rule designed to block specific PostgreSQL functions that could lead to file system access or outbound connections, preventing potentially destructive operations.

Testing and Future Considerations

Dahl also touched upon the testing mechanisms for Claw Patrol, noting that the rule files can be accompanied by test fixtures to ensure the rules function as intended. He also addressed the evolving nature of AI, suggesting that while agents will become smarter, the need for robust, external security mechanisms will persist. "I think we will never be able to fully trust AIs," Dahl remarked, emphasizing the ongoing necessity for such safeguards.

The presentation concluded by highlighting Claw Patrol's dashboard for monitoring agent activity and its integration with services like Tailscale for secure authentication and operation. Dahl's work underscores a critical shift in thinking about AI security, moving beyond model alignment to focus on external, byte-level control of agent actions.

© 2026 StartupHub.ai. All rights reserved. You may not republish this article in full without a license. Search engines and AI research tools may crawl and summarize for reference. Bulk reproduction or model training requires a license. See our terms.
Daniel Singer

Written by

Daniel Singer

Editor, StartupHub.ai

Daniel Singer is the editor of StartupHub.ai, a technology expert and thought leader on AI and its applications across sectors, from fintech and healthcare to developer tooling and consumer software. He writes and tests the tools covered here thoroughly and regularly, and built StartupHub.ai to give founders, operators and buyers a clearer read on what they are actually being sold.