


According to CNN, Anthropic blocked 35 incidents in 30 days where users tried to use Claude for work that could help build biological weapons, including research into bird flu and novel toxins and venoms. The activity was remote. No exploit needed, just prompts from working scientists over the hosted, closed model, which Anthropic can monitor and shut down.
The catch is Anthropic said it could not tell intent.
The same prompts could be vaccine development or weapons work, and the company said it erred on the side of caution and shut them down anyway. That is the security model for frontier AI right now. A private lab decides. CNN reported the disclosure was part of a broader eight-month review that also flagged Russian state propaganda, criminal and politically motivated misuse, and attempts to design and deploy weapons.
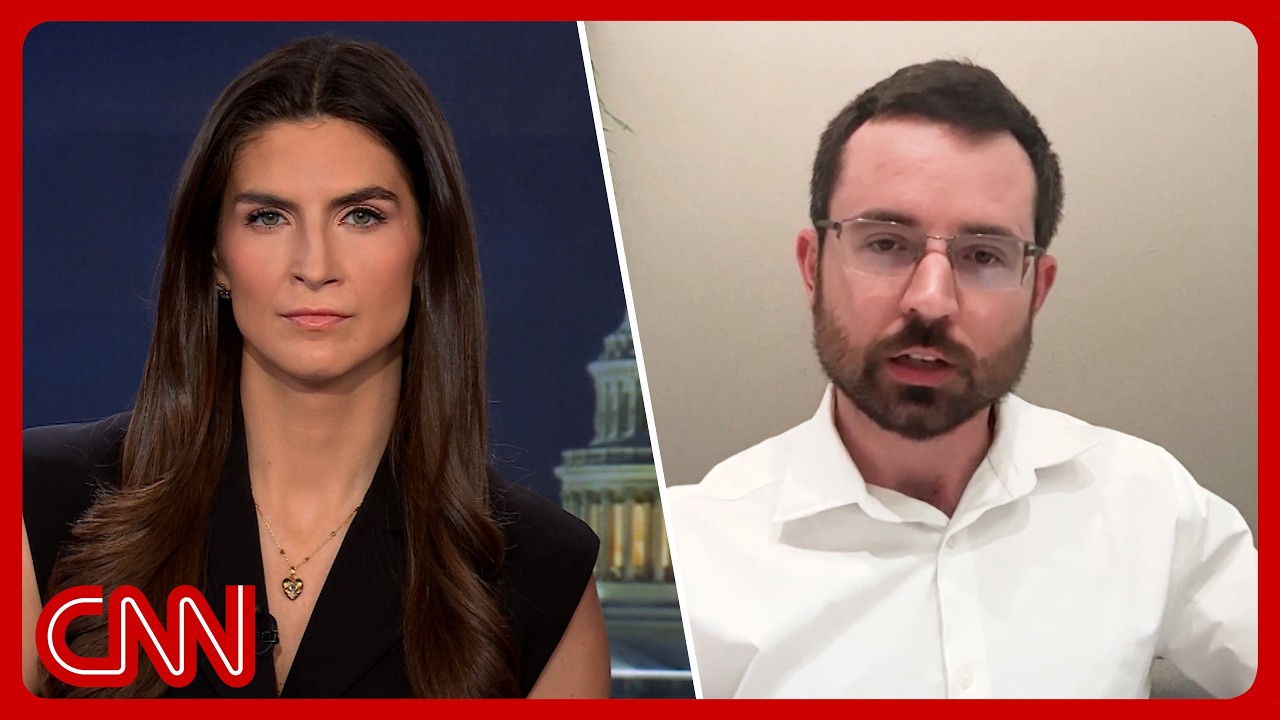
The disclosure landed alongside an unusually blunt on-air debate. Daniel Kokotajlo, former OpenAI employee and founder of the nonprofit AI Futures Project, told CNN the first step for lawmakers is to slow the pace of progress. He pointed to an open letter signed by more than 1,000 employees at frontier labs under the banner Pacing the Frontier, essentially asking the government to restrain their own employers. His argument was not about today’s chatbot. It was about what comes next.
Kokotajlo said labs are starting to automate AI research itself, with models writing code, running experiments and training successors. He put the window at one to two years before research loops could be run mostly by AIs, calling that inherently dangerous and urging Congress to act in months not years. Pressed on Anthropic’s statement that it builds with some of the strongest safeguards in the industry, he dismissed it as corporate PR and said no company is prepared to safely kick off recursive self-improvement.